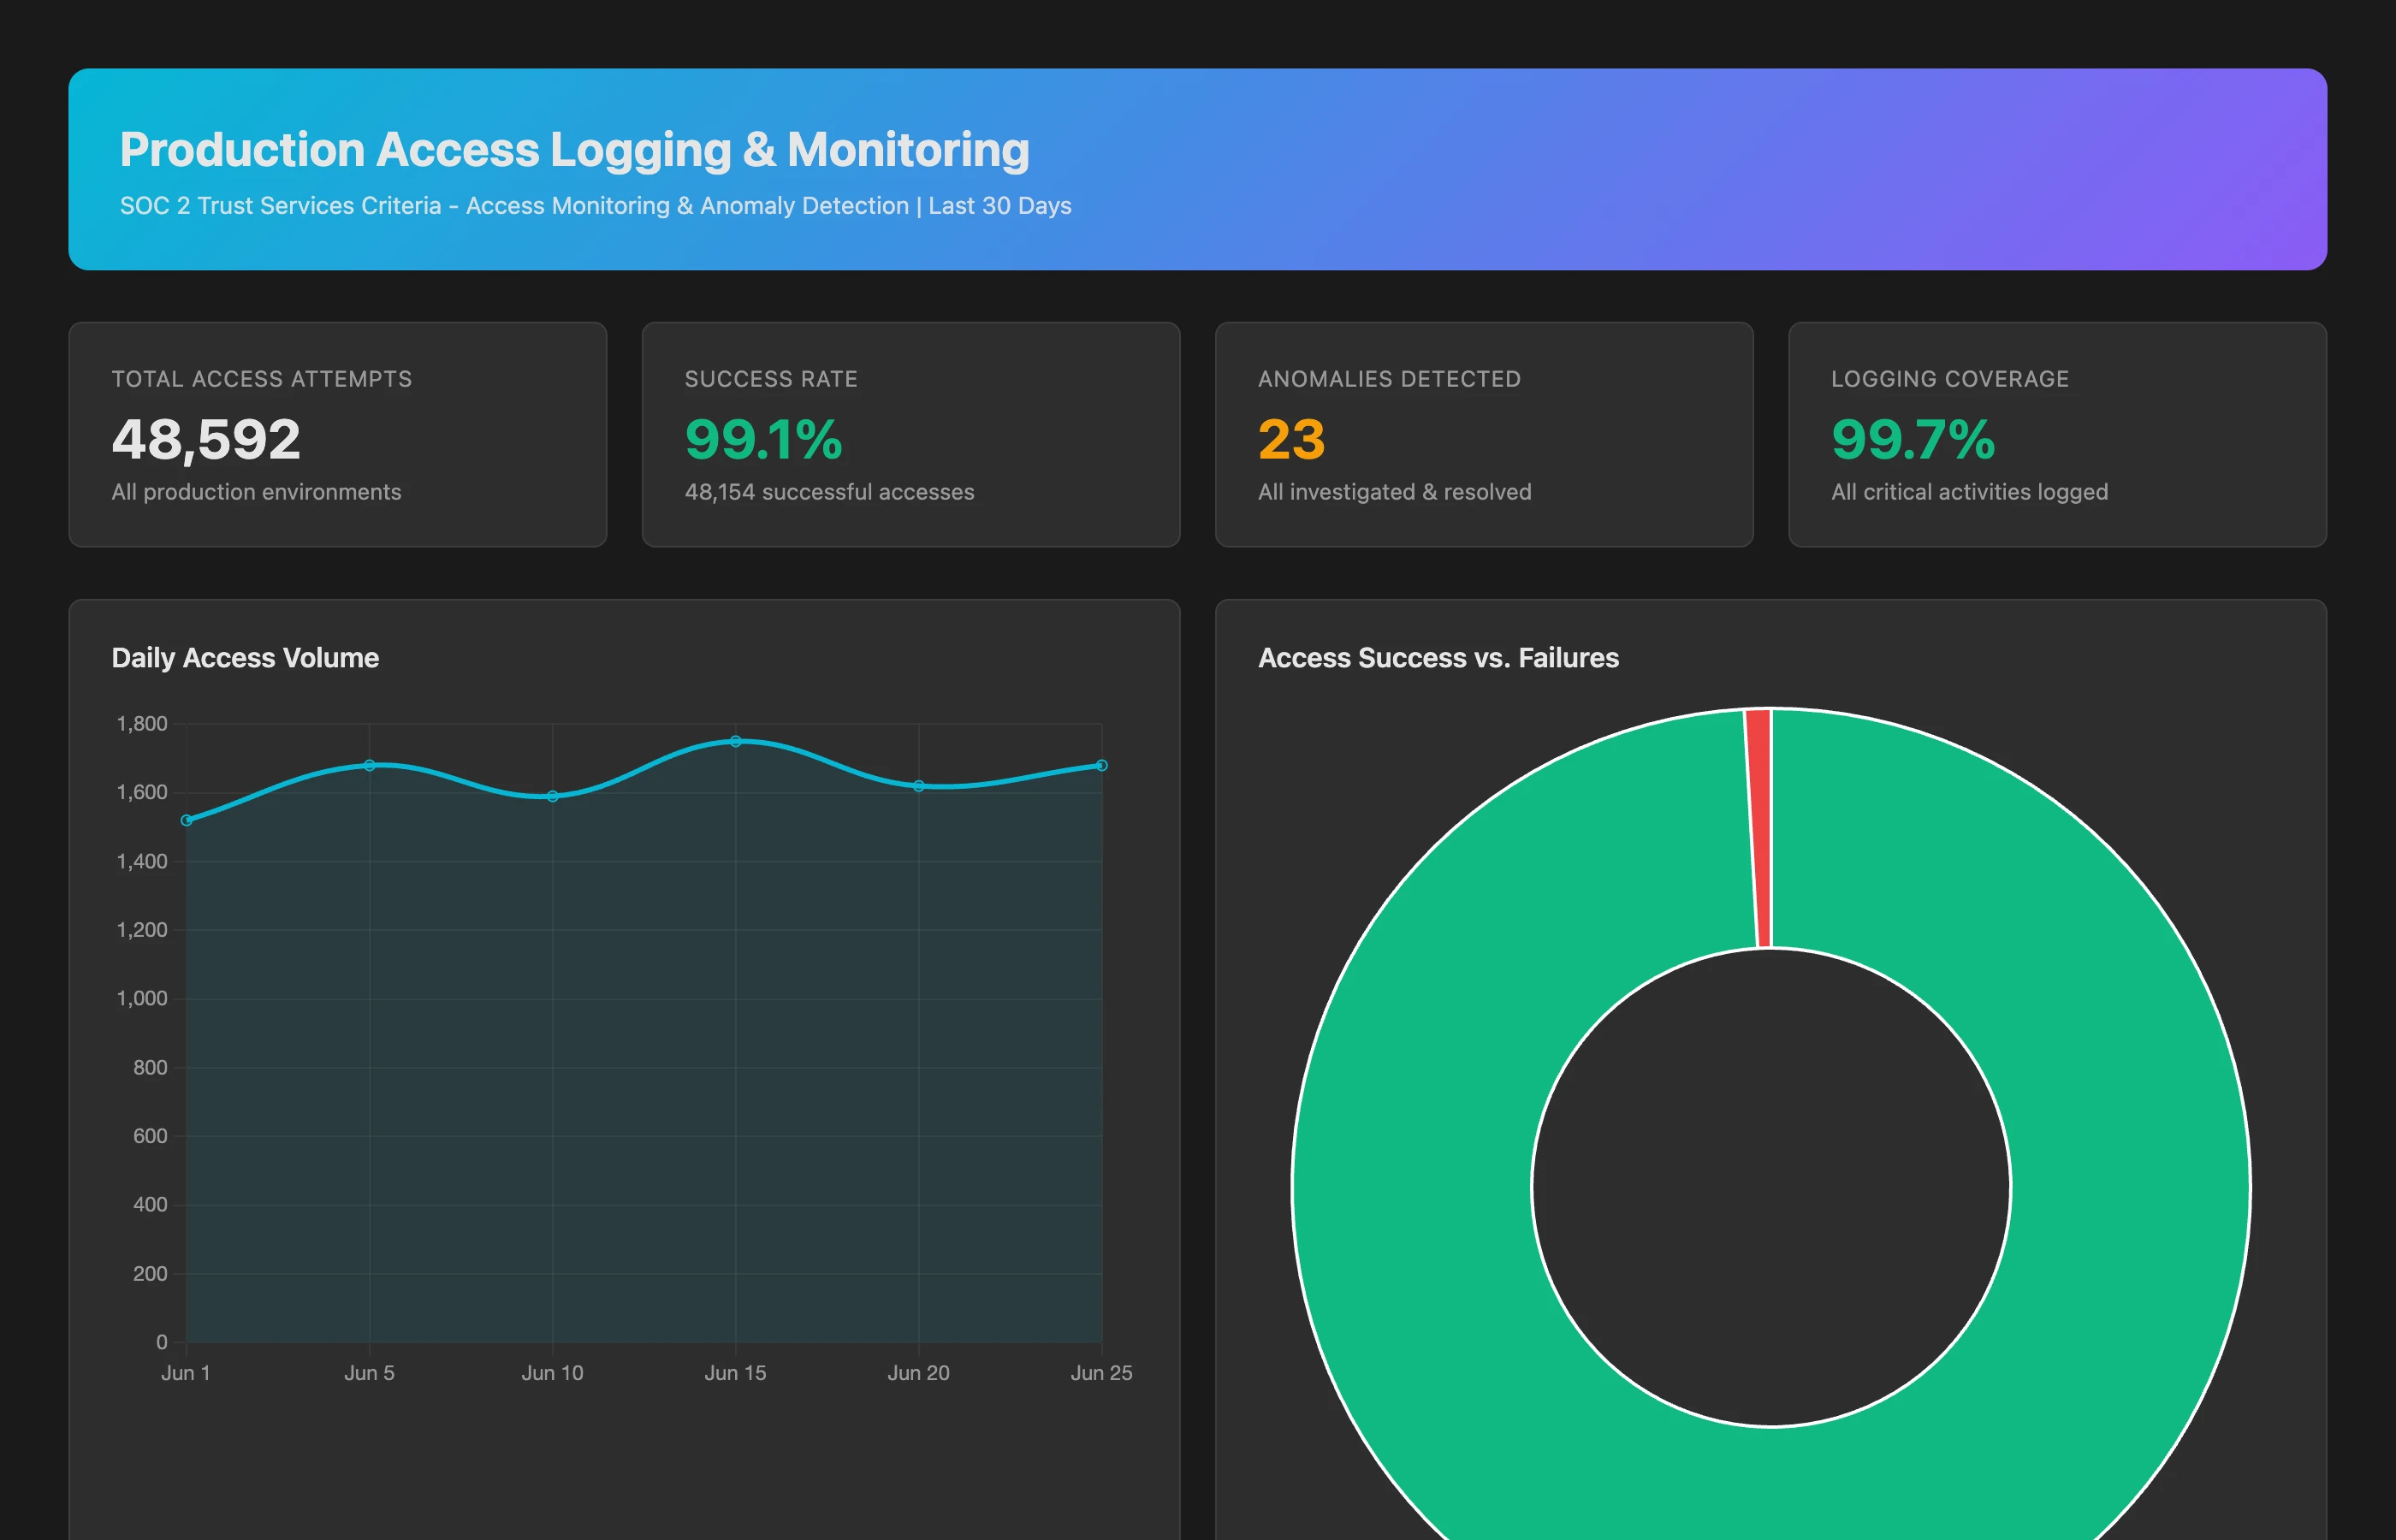
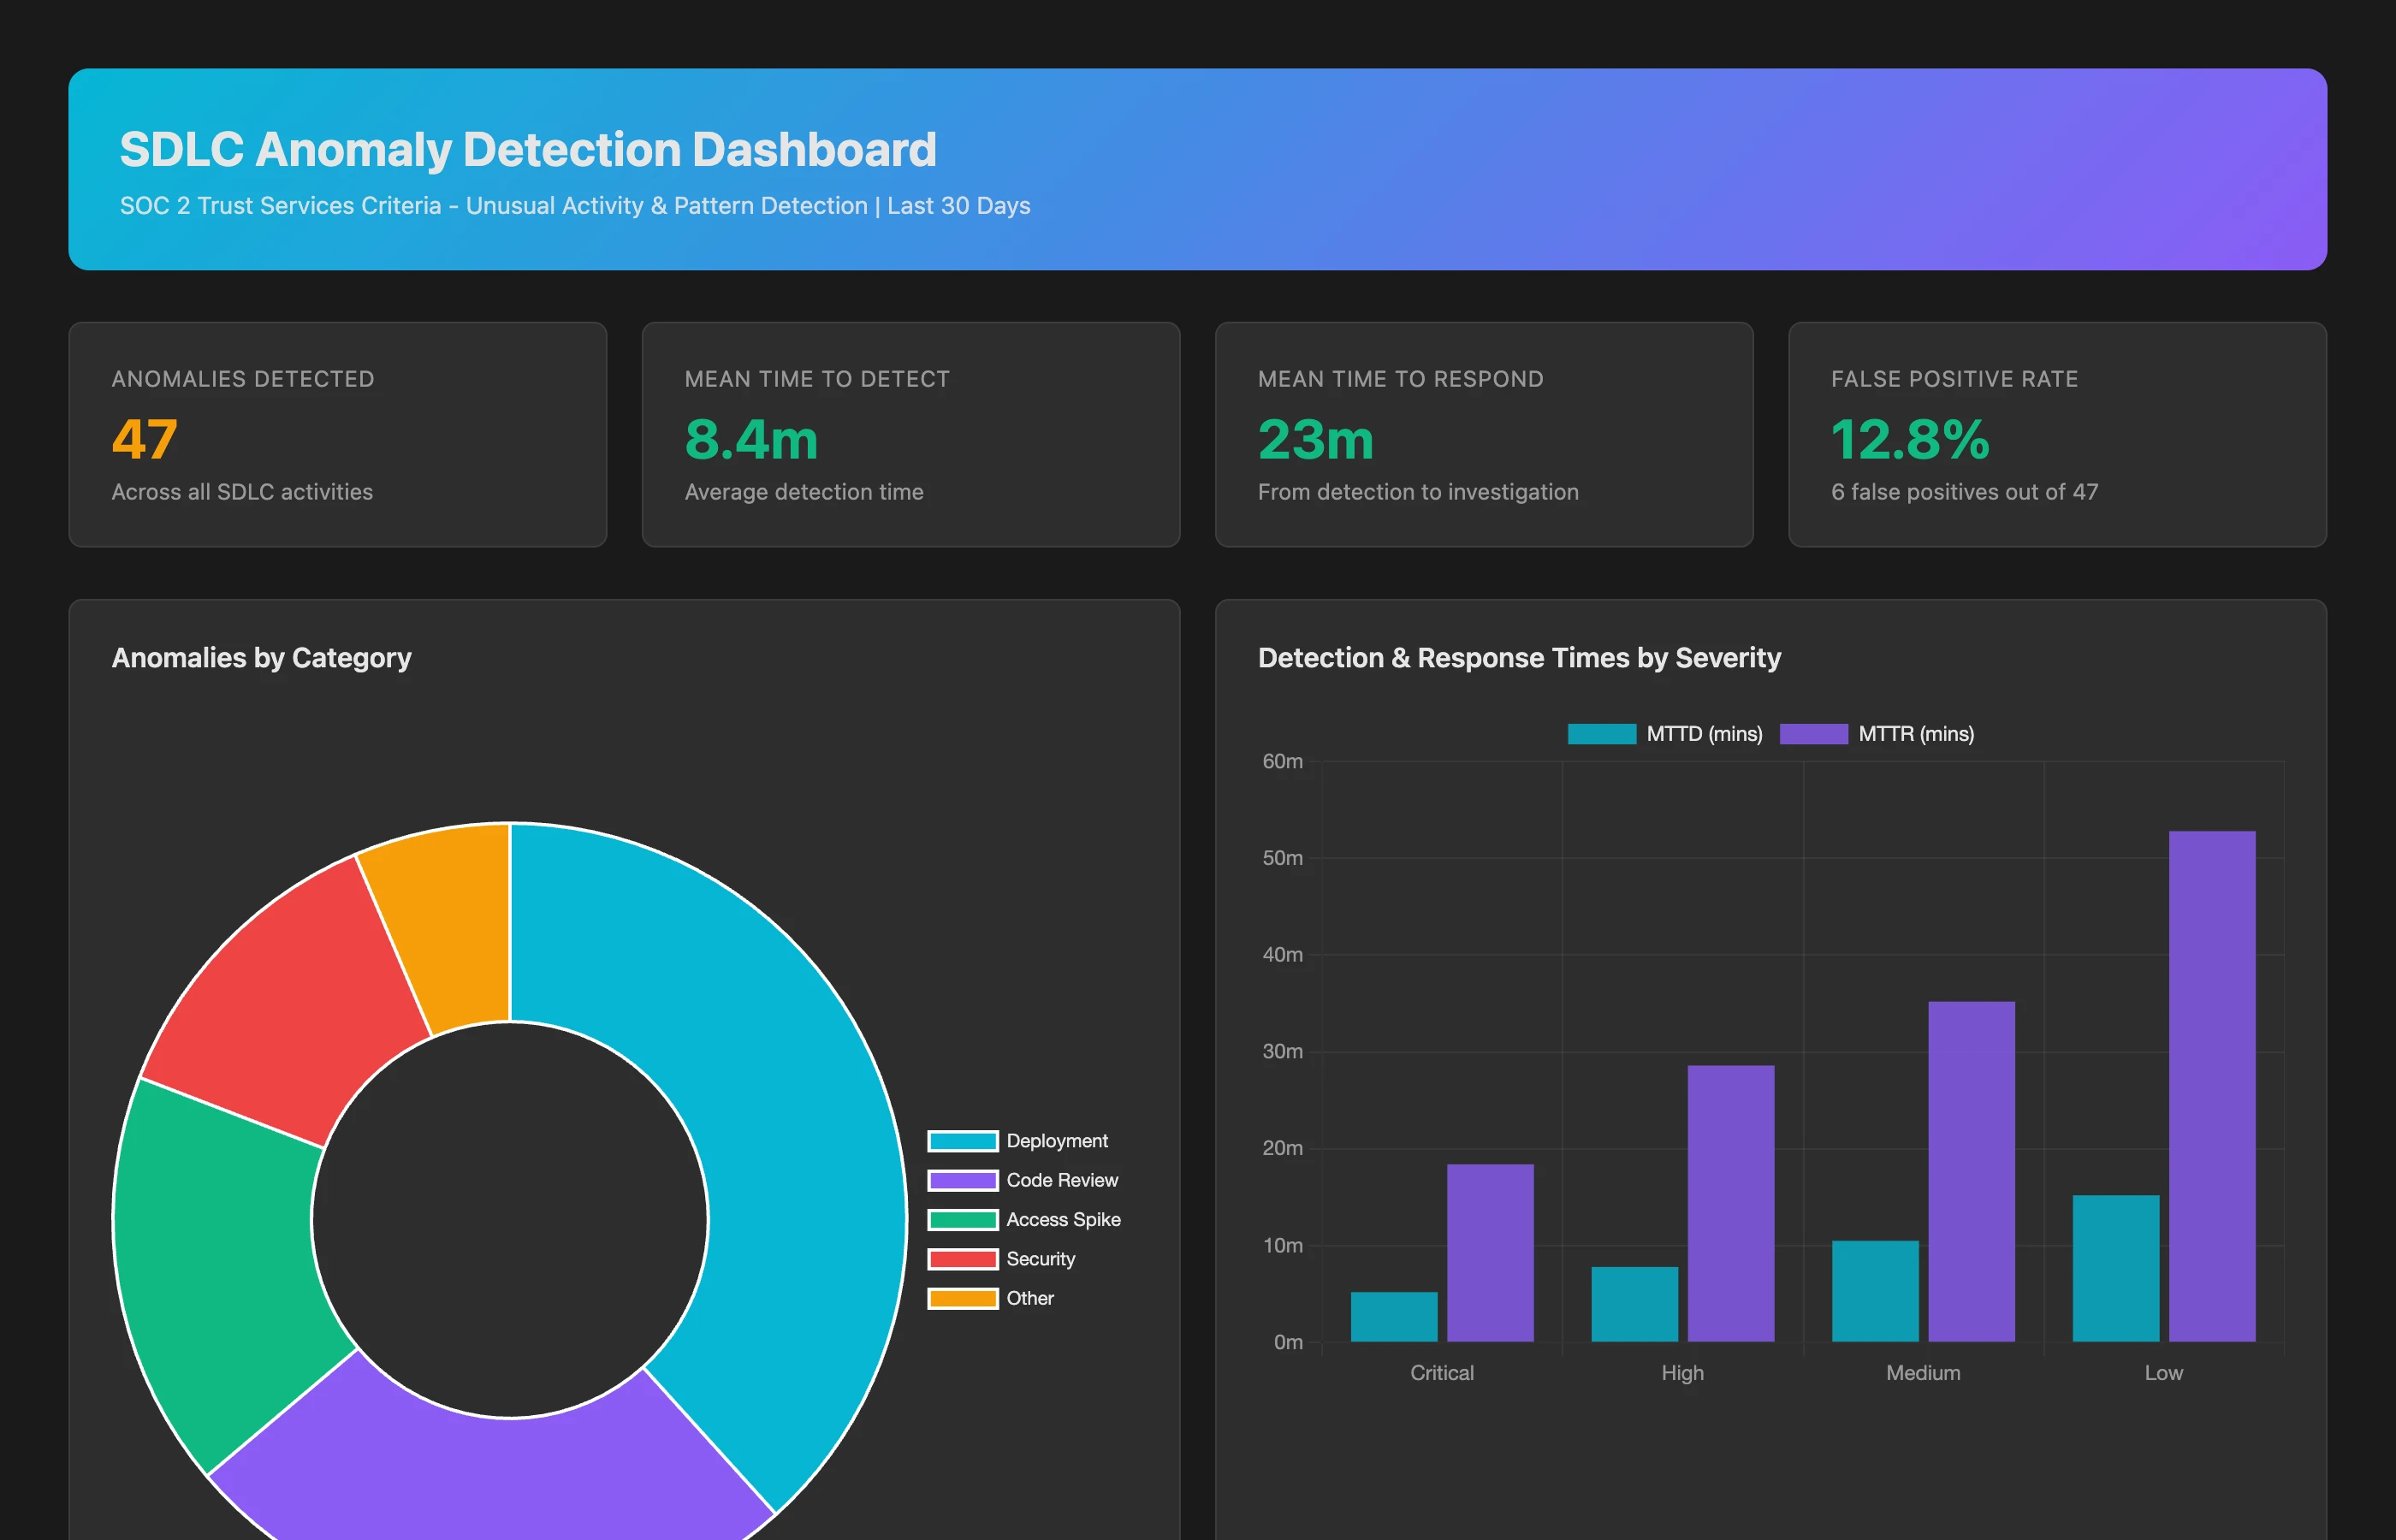
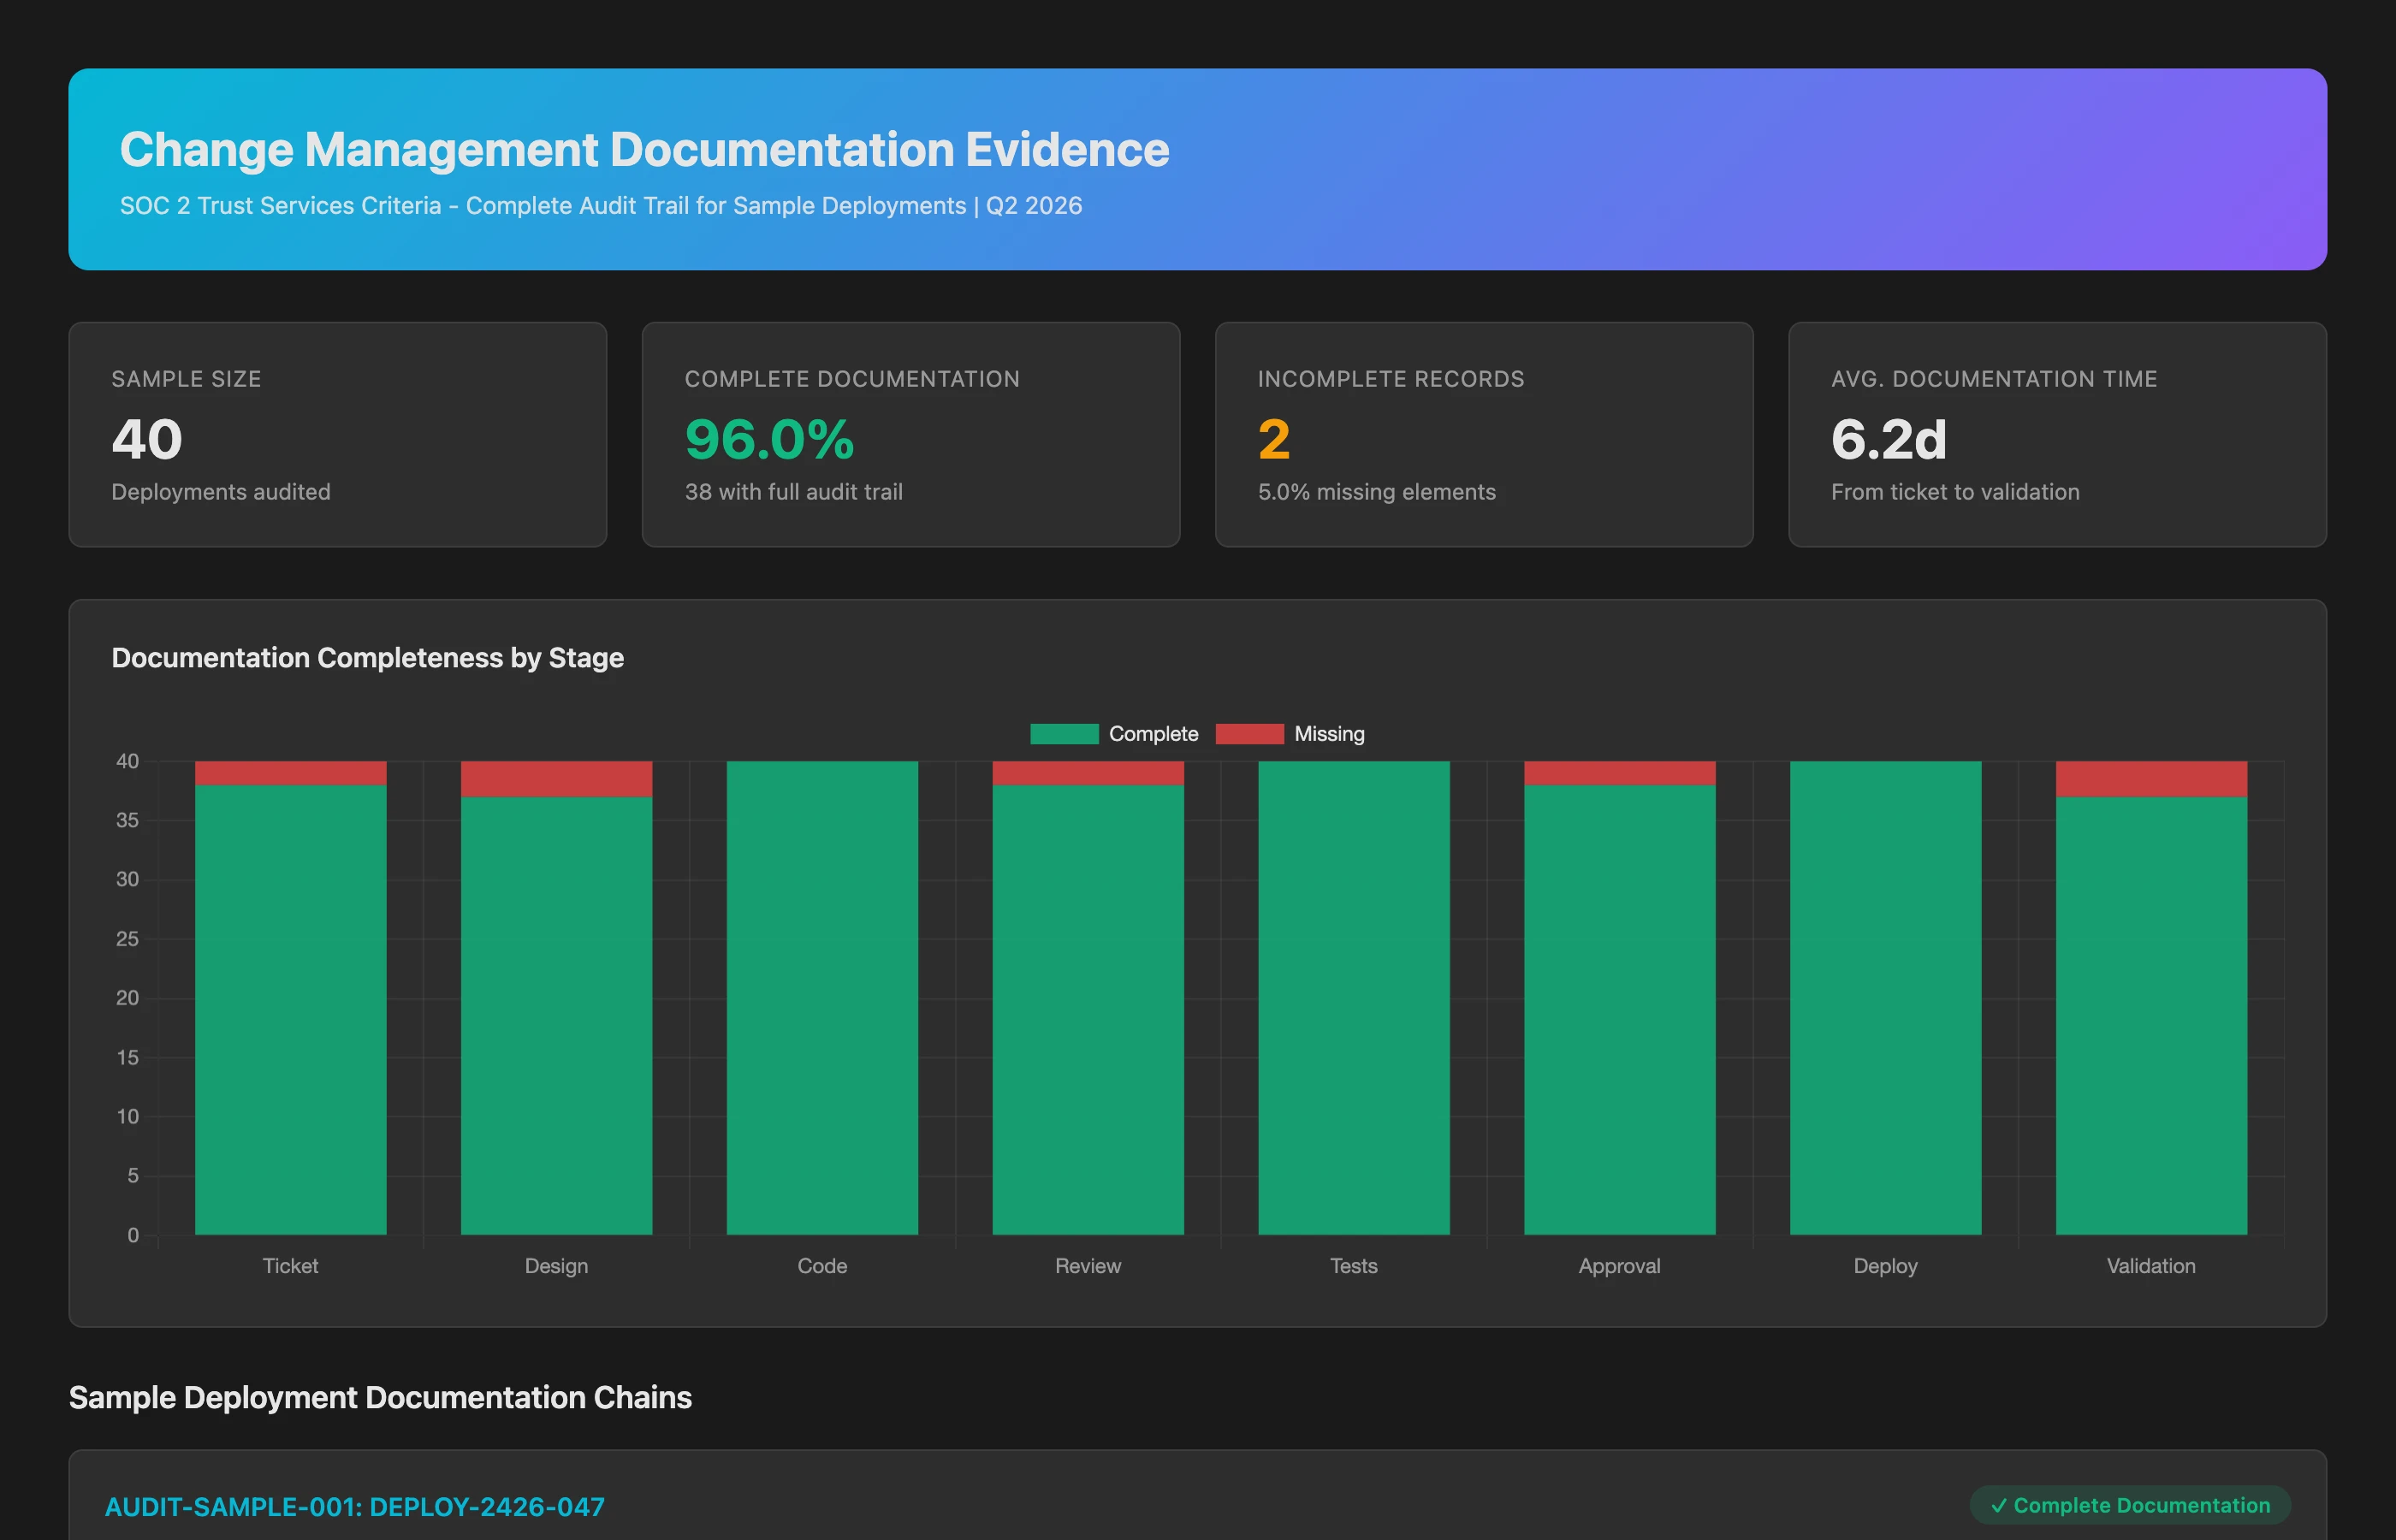
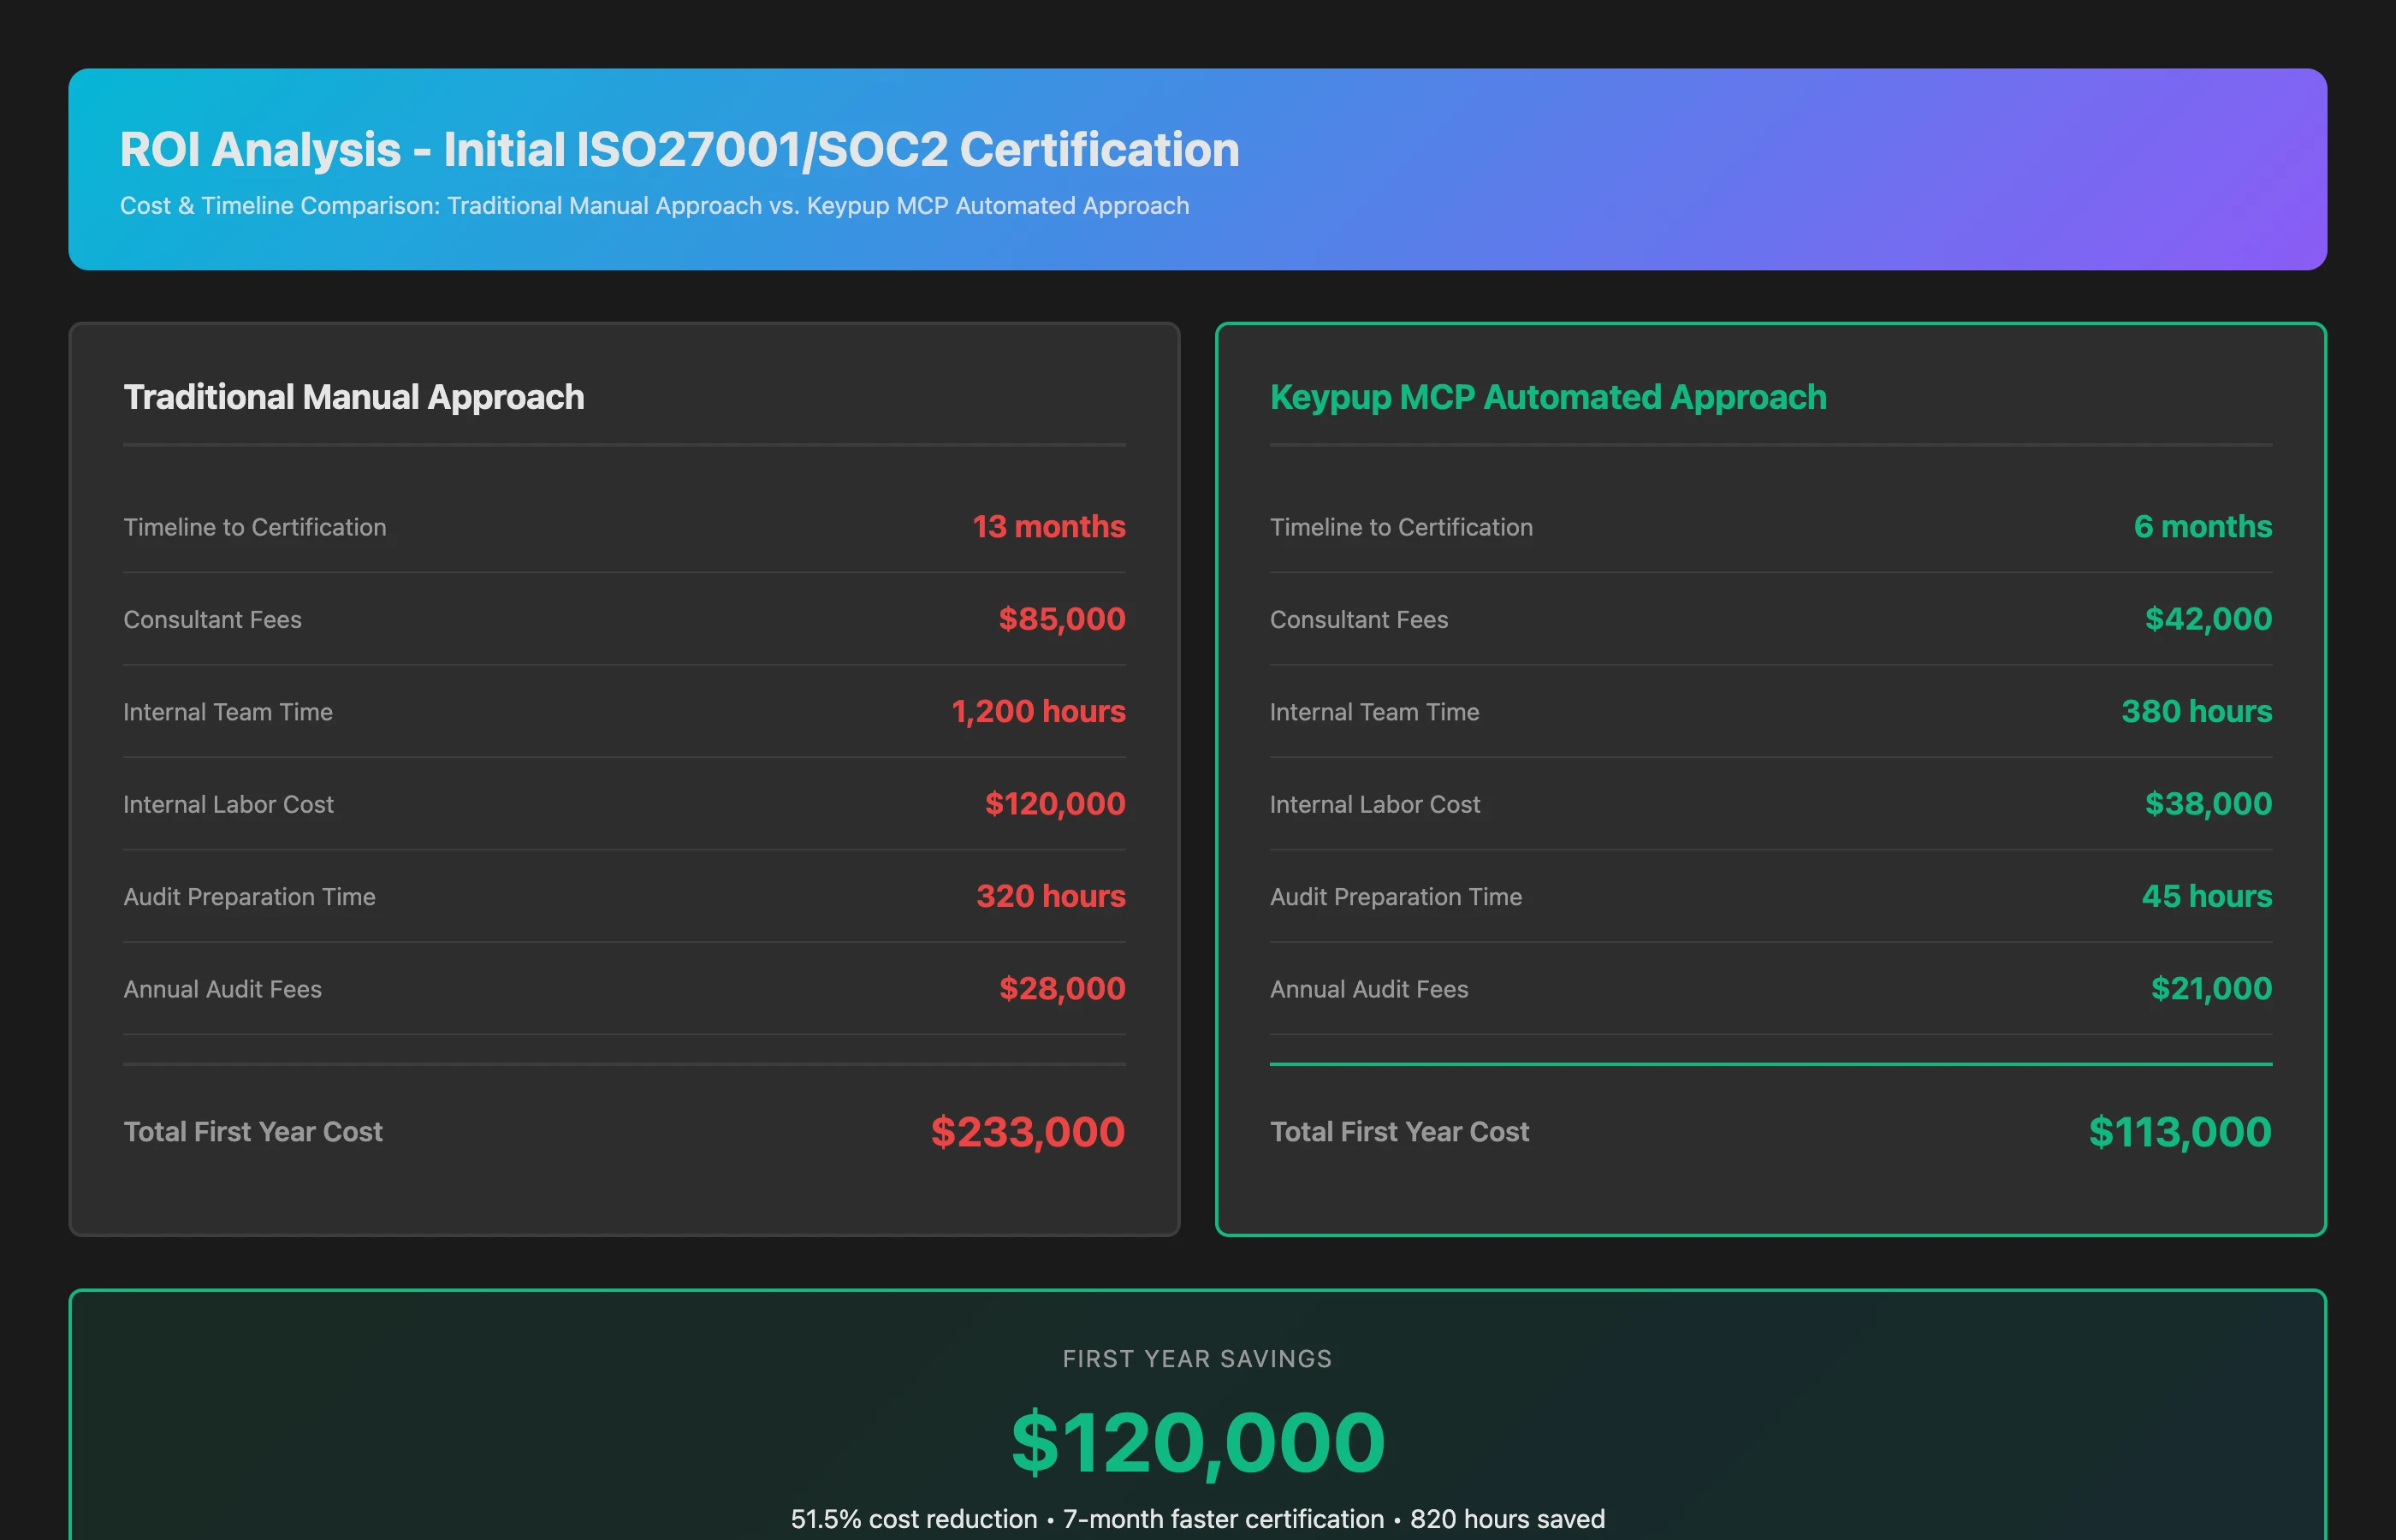
TL;DR: ISO27001 and SOC2 Type II certifications are increasingly critical for software companies, but the SDLC-specific requirements—access control audits, change management traceability, vulnerability response times, and continuous monitoring—create massive documentation burdens. Traditional approaches require 6-12 months of manual evidence collection, costing $150K-$400K annually. Keypup covers the part of that evidence that lives in your Git hosts and work trackers: its compliance dashboards (built from a template or by the AI Agent) keep code review, approval and change traceability controls visible all year, and its read-only MCP Server answers auditor questions in plain language from Claude, ChatGPT or Cursor.
- Key Point 1: ISO27001 (A.8.32, A.8.8) and SOC2 CC8.1 require detailed SDLC controls including code review audits, change authorization trails, and vulnerability remediation tracking. Code review, approval and change records live in your GitHub/GitLab/Bitbucket/Azure DevOps and Jira data but are difficult to extract and format for auditors; access logs and deployment records live in other systems.
- Key Point 2: Compliance dashboards in Keypup turn certification from a painful annual audit sprint into an always-ready state: the data syncs continuously from your tools, you review the dashboard weekly, and you answer an auditor's sample request with an on-demand query instead of a one-off script.
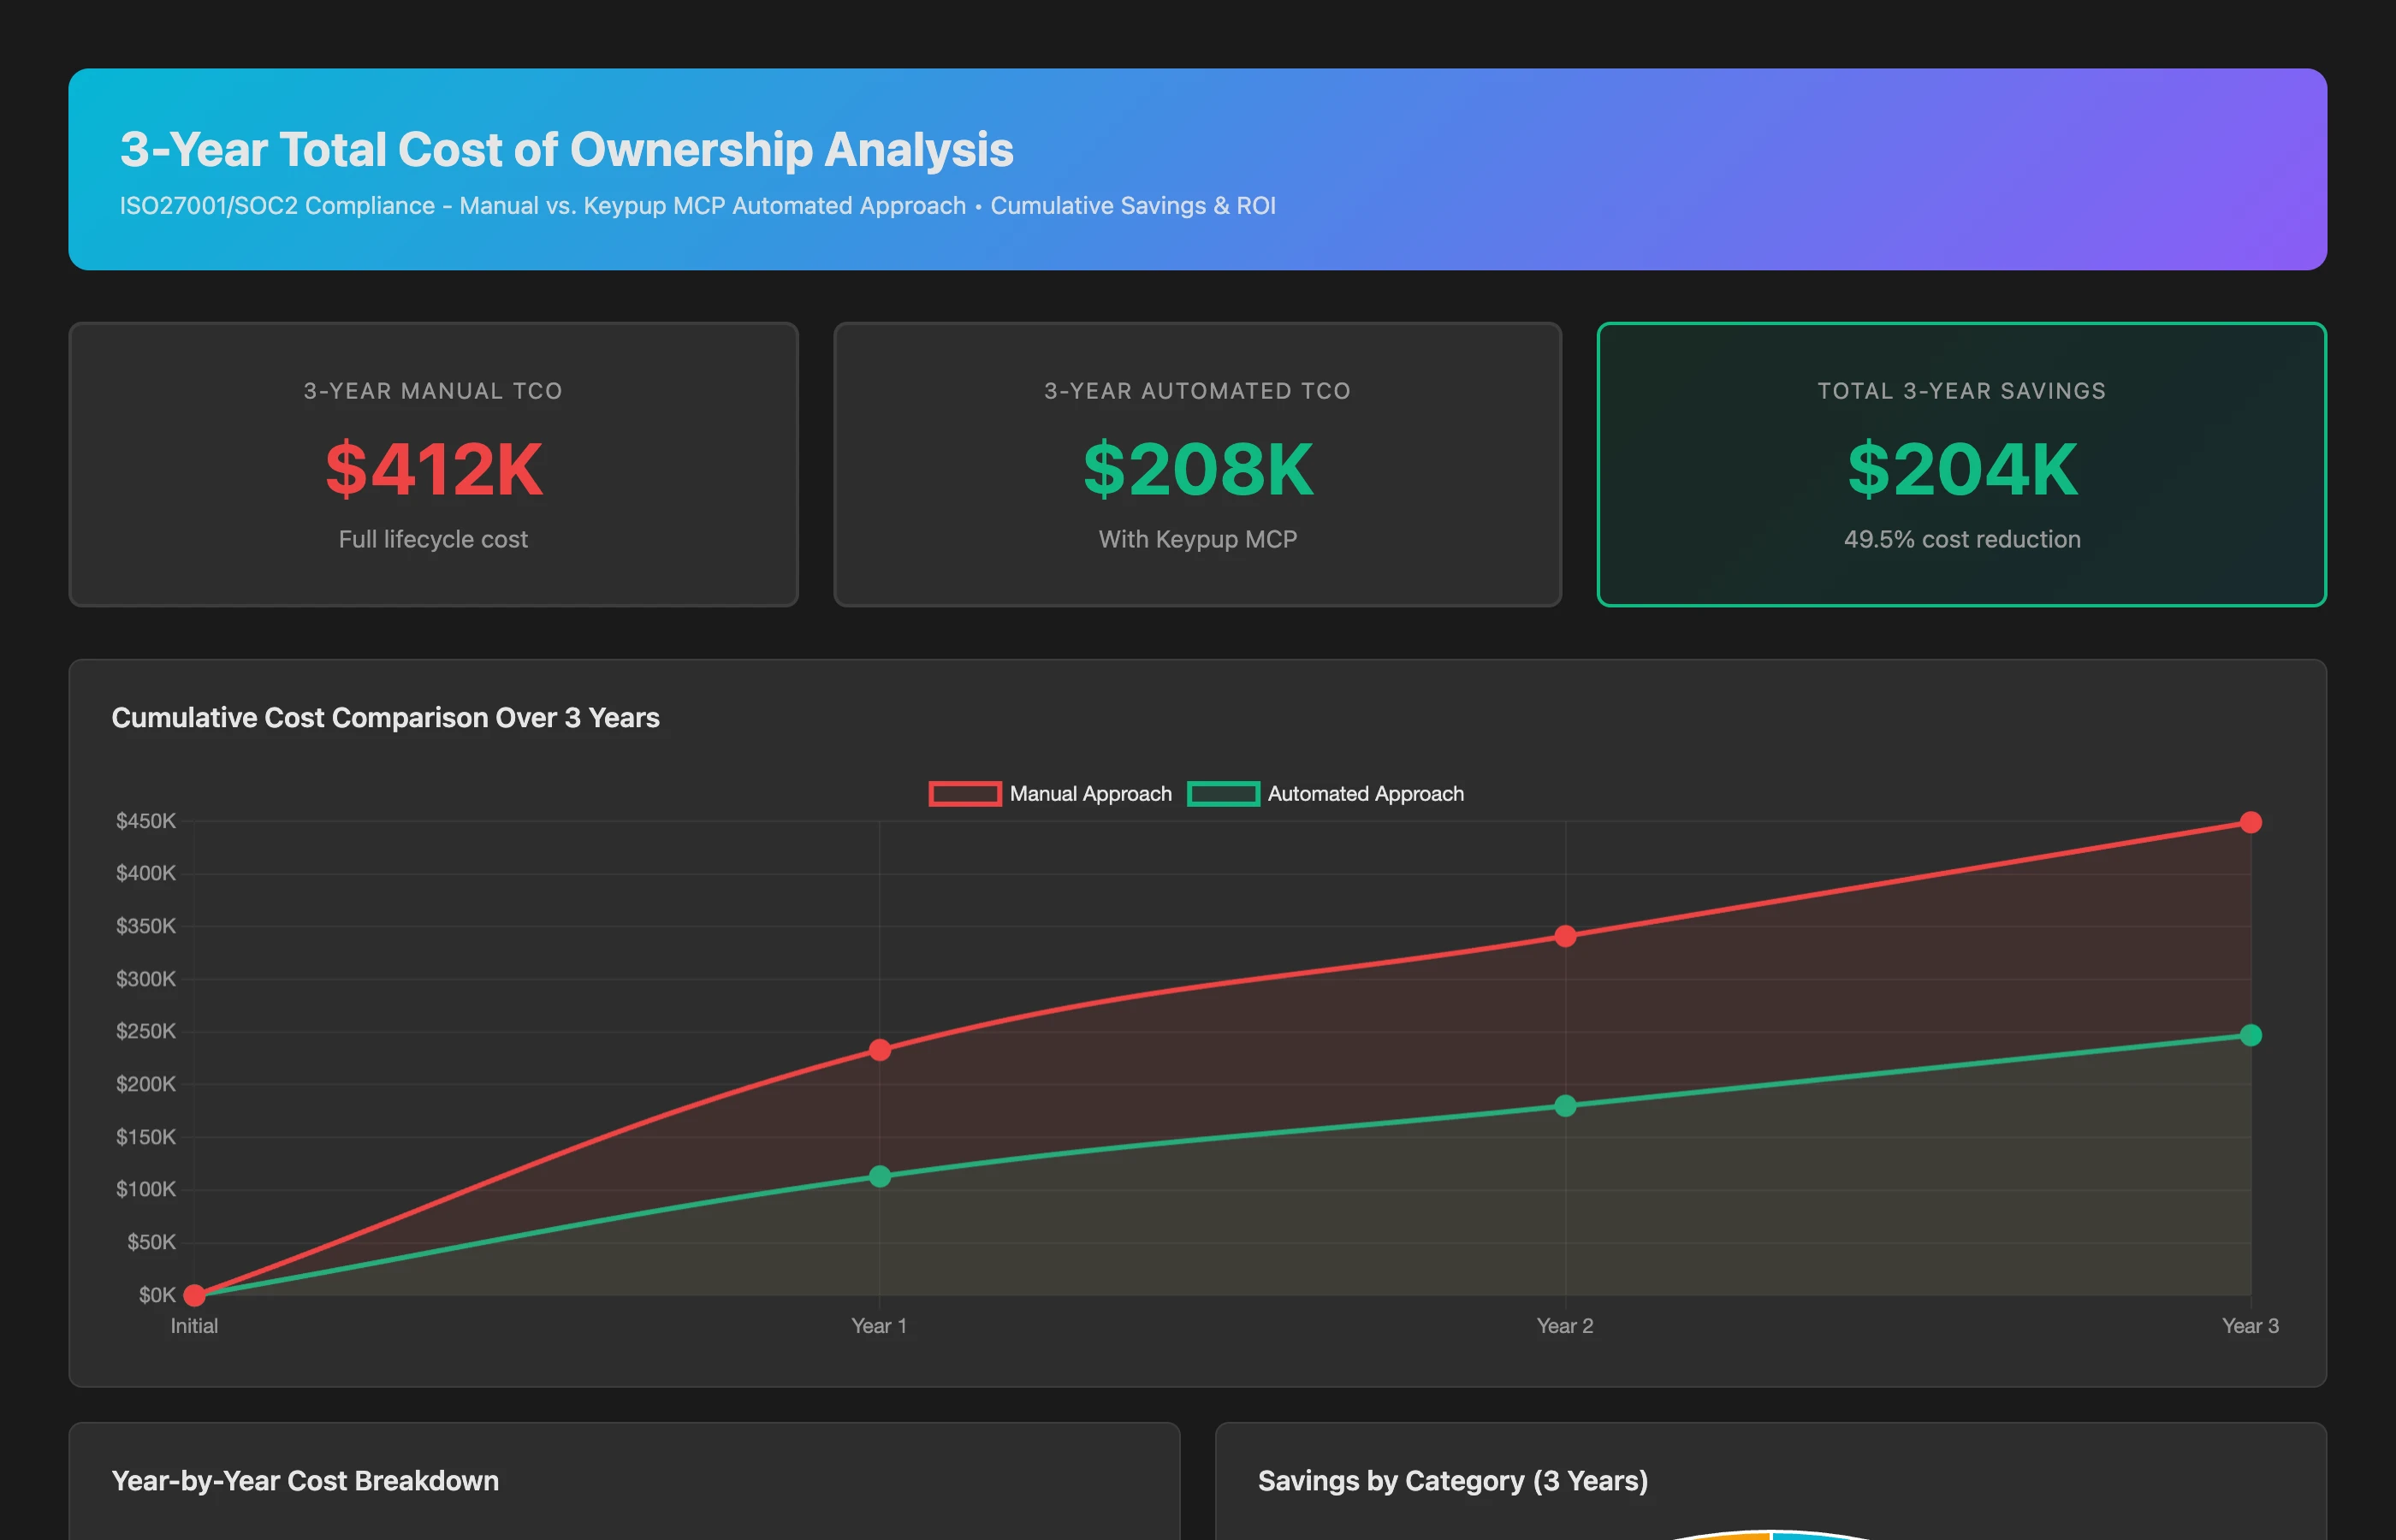
- Key Point 3: The ROI of automated SDLC evidence can be substantial. Our illustrative estimate below (a hypothetical calculation, not measured customer results) shows how cutting manual evidence collection reduces internal time and consultant hours.
Introduction: When Security Certifications Meet Software Development Reality
Your sales team just lost a $2M enterprise deal. The reason? "We need to see your ISO27001 certification before we can proceed." Your CFO is pushing for SOC2 Type II to unlock Series B funding. Your head of security is drowning in spreadsheets trying to document your software development lifecycle for auditors.
Welcome to the modern software company dilemma: security certifications are no longer optional nice-to-haves—they're mandatory tickets to market. But achieving and maintaining ISO27001 and SOC2 Type II compliance creates a special challenge for engineering organizations because these frameworks impose extensive requirements on how you develop, deploy, and manage software.
The problem isn't that your engineering practices are inadequate. Most well-run development teams already implement the security controls these frameworks require: code reviews, access management, change control, vulnerability patching, deployment tracking. The problem is proving it to auditors in the specific format they demand.
We spent 8 months preparing for our SOC2 Type II audit. Our engineering practices were solid—mandatory code review, role-based GitHub access, automated security scanning—but we had to manually reconstruct 12 months of evidence. Every week, our compliance consultant asked for things like 'proof that all PRs affecting production were reviewed by authorized personnel' or 'demonstrate your mean time to remediate critical vulnerabilities.' We'd spend hours writing scripts to extract data from GitHub and Jira, format it into spreadsheets, then explain why our metrics showed we met the controls. It was exhausting and expensive.
This article provides a comprehensive guide to achieving ISO27001 and SOC2 Type II certification for software development organizations, with specific focus on:
- What these certifications actually require from your SDLC
- The specific controls and evidence auditors expect from engineering teams
- How traditional manual approaches waste time and create ongoing compliance debt
- How Keypup dashboards and the Keypup MCP Server automate SDLC evidence for code review, change management and remediation controls
- Concrete examples and an illustrative ROI estimate showing potential time and cost savings
Whether you're preparing for your first certification audit or struggling with annual recertification overhead, this guide will show you how to transform compliance from a painful burden into an automated, always-ready capability.
A note on where we stand: Keypup itself holds ISO 27001 certification and a SOC 2 Type II report, so the practices below are ones we apply to our own SDLC. You can review our controls on the Keypup Trust Center and our security page.
Understanding ISO27001 and SOC2 Type II: What They Are and Why They Matter
Before diving into implementation, let's clarify what these certifications are, how they differ, and why both are increasingly essential for software companies.
ISO27001: The International Security Management Standard
ISO/IEC 27001 is an international standard for information security management systems (ISMS). Published by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC), it provides a systematic approach to managing sensitive company information.
Key characteristics:
- Certification-based: Third-party auditors certify your ISMS against the standard
- Risk-focused: Requires identifying risks and implementing appropriate controls
- Comprehensive: Covers 93 controls across 14 categories (Annex A)
- Global recognition: Accepted worldwide, especially strong in Europe and APAC
- Annual surveillance audits: Recertification every 3 years with annual checks
Why it matters for software companies:
- Enterprise procurement requirement: Many large enterprises (especially European) require ISO27001 from vendors
- Regulatory compliance: Helps satisfy GDPR, NIS2, and other security regulations
- Risk management framework: Provides structured approach to security
- Competitive advantage: Demonstrates commitment to security best practices
SOC2 Type II: The Trust Services Criteria Standard
SOC 2 (Service Organization Control 2) is a US-based auditing standard developed by the American Institute of CPAs (AICPA) that evaluates how service organizations handle customer data. Type II specifically examines operational effectiveness over time (typically 6-12 months).
Key characteristics:
- Report-based: Produces a confidential audit report (not a certificate)
- Trust Services Criteria: Evaluates Security (mandatory), plus optional Availability, Processing Integrity, Confidentiality, Privacy
- US-focused: Required by US enterprises, increasingly global
- Operational evidence: Type II requires 6-12 months of operational data
- Annual audits: Most companies recertify annually
Why it matters for software companies:
- US market access: Essential for selling to US enterprises and government
- Investor requirement: Many VCs require SOC2 before Series B funding
- Customer trust: Demonstrates operational security maturity
- Due diligence: Satisfies security questionnaires and assessments
ISO27001 vs. SOC2: Complementary, Not Competing
Many companies pursue both certifications because they serve different markets and purposes:
| Aspect | ISO27001 | SOC2 Type II |
| Origin | International (ISO/IEC) | US (AICPA) |
| Primary Markets | Europe, APAC, Global | US, increasingly global |
| Output | Certificate | Confidential report |
| Focus | ISMS framework | Operational controls |
| Audit Scope | Point-in-time + surveillance | 6-12 months operational |
| Public Disclosure | Certificate number public | Report shared under NDA |
| Industry Preference | General business | Tech/SaaS |
The overlap: Both require similar SDLC controls (access management, change control, security testing, incident response), which means implementing controls for one largely satisfies the other.
The differences: ISO27001 emphasizes documented procedures and risk assessments; SOC2 emphasizes operational evidence proving those procedures actually work over time.
The SDLC Requirements: What Auditors Actually Want to See
Both ISO27001 and SOC2 Type II impose specific requirements on software development lifecycle activities. Let's break down the key controls that engineering teams must demonstrate.
ISO27001 Annex A Controls for Software Development
The most relevant ISO27001 controls for software development organizations include:
A.8.31 - Separation of Development, Test and Production Environments
- Requirement: Development, testing, and production environments must be separated and protected
- What auditors want: Evidence that developers cannot deploy directly to production, production data is protected, and access is role-based
A.8.32 - Change Management
- Requirement: Changes to information processing facilities and systems shall be subject to change management procedures
- What auditors want: Documented change approval process, traceability from requirements to deployment, rollback procedures
A.5.15 - Access Control
- Requirement: Access to information and systems shall be controlled on a business need-to-know basis
- What auditors want: Evidence of least-privilege access, regular access reviews, access removal when roles change
A.5.16 - Identity Management
- Requirement: The full lifecycle of identities shall be managed
- What auditors want: User provisioning/deprovisioning logs, authentication controls, MFA implementation
A.8.8 - Management of Technical Vulnerabilities
- Requirement: Information about technical vulnerabilities shall be obtained and managed
- What auditors want: Vulnerability scanning process, remediation tracking, mean time to patch critical vulnerabilities
SOC2 Trust Services Criteria for Software Development
The most relevant SOC2 criteria for engineering teams include:
CC6.1 - Logical and Physical Access Controls
- Requirement: The entity implements logical access security software, infrastructure, and architectures
- What auditors want: Evidence of authentication mechanisms, role-based access, and access logging
CC6.6 - Logical Access Control - Restrict Access
- Requirement: Prior to issuing system credentials, the entity registers and authorizes new users
- What auditors want: User provisioning workflow, access approval records, periodic access reviews
CC6.8 - Logical Access Control - Prevent and Detect Unauthorized Access
- Requirement: The entity restricts access to system configurations and settings
- What auditors want: Evidence that production access is logged, monitored, and reviewed
CC7.2 - System Monitoring - Detect and Respond
- Requirement: The entity monitors system components and the operation of those components for anomalies
- What auditors want: Security monitoring logs, incident detection mechanisms, response procedures
CC8.1 - Change Management - Document Changes
- Requirement: The entity authorizes, designs, develops or acquires, configures, documents, tests, approves changes
- What auditors want: Change request records, approval workflows, testing evidence, deployment logs
The Evidence Burden: What You Must Produce for Auditors
For both certifications, auditors will request evidence demonstrating that your controls operate effectively. Common requests include:
Access control audit trail: "Show me all individuals who had production access during the audit period, when access was granted, who approved it, and when it was revoked when they changed roles."
Code review evidence: "Demonstrate that 100% of production code changes were reviewed by authorized personnel before deployment."
Change management traceability: "For these 10 randomly selected production deployments, show me the associated Jira ticket, code review, approval, and deployment log."
Vulnerability remediation tracking: "Show me all critical vulnerabilities detected in the last 12 months, their severity scores, when they were detected, and your mean time to remediation."
Incident response records: "Provide all security incidents in the last year, including detection time, response actions, resolution time, and root cause analysis."
Separation of duties: "Prove that developers cannot approve their own code or deploy without review."
Access reviews: "Show quarterly access review reports demonstrating that production access was validated and inappropriate access was revoked."
The challenge: all this data exists in your GitHub, Jira, PagerDuty, and security tools—but extracting it, formatting it consistently, and presenting it in audit-ready form requires enormous manual effort.
The Traditional Approach: Manual Evidence Collection and Its Costs
Before we explore automated solutions, let's understand the traditional manual approach and why it's so expensive and time-consuming.
The Manual Certification Process
A typical ISO27001 or SOC2 Type II certification journey looks like this:
Phase 1: Gap Analysis (2-3 months)
- Hire compliance consultant ($15K-$40K)
- Map existing SDLC practices to framework requirements
- Identify control gaps and create remediation plan
- Implement missing controls (MFA, logging, access reviews, etc.)
Phase 2: Documentation (3-4 months)
- Write policies and procedures for all required controls
- Document SDLC workflows (code review, deployment, incident response)
- Create evidence collection procedures
- Train engineering team on compliance requirements
Phase 3: Evidence Collection (2-4 months)
- Manually export data from GitHub, Jira, and other tools
- Write scripts to analyze PRs, deployments, access logs
- Format data into spreadsheets auditors can review
- Create narrative explanations for each control
Phase 4: Audit (1-2 months)
- Auditor requests samples and evidence
- Team scrambles to find requested data
- Multiple rounds of clarifications and additional evidence
- Remediate any findings before final report
Total timeline: 8-13 months Total cost: $150K-$400K (consultant fees + internal time + audit fees)
The Ongoing Maintenance Burden
Once certified, the pain doesn't end. Annual recertification requires:
- Continuous evidence collection: Someone must regularly export and archive SDLC data
- Quarterly access reviews: Manually audit who has production access
- Incident documentation: Every security event must be logged and analyzed
- Change control audits: Sample deployments and trace back to approvals
- Surveillance audits: Annual re-audits to maintain certification
Annual maintenance cost: $80K-$150K (ongoing consultant fees + internal overhead + audit fees)
Our first SOC2 audit took 11 months and cost us $280K between consultant fees and internal time. But the ongoing maintenance is worse—we have one engineer spending 20% of their time on 'compliance work,' which is really just exporting GitHub data, building evidence spreadsheets, and responding to auditor requests. That's $60K in engineering salary annually just to maintain compliance. And every time an auditor asks for a new data cut, we write another one-off script.
Why Manual Approaches Fail at Scale
The manual approach creates several problems:
Point-in-time compliance: Evidence is collected for audits, creating a scramble every year rather than continuous readiness
Data fragmentation: Evidence lives across GitHub, Jira, PagerDuty, Slack, requiring integration scripts for each audit
Inconsistent formatting: Each auditor wants data formatted differently, requiring rework
No real-time visibility: Compliance team doesn't know if controls are working until they check manually
High overhead: Significant ongoing effort diverts engineering resources from product development
Human error: Manual data collection and analysis introduces errors that auditors flag
Lack of trend analysis: Difficult to track compliance posture over time or identify degrading controls
The solution: automated, continuous compliance monitoring that treats certification as an operational capability, not a periodic event.
Keypup: Continuous SDLC Evidence for ISO27001 and SOC2
Keypup turns the SDLC part of ISO27001 and SOC2 Type II compliance from a manual burden into an always-ready capability: your development data syncs continuously into Keypup, compliance dashboards keep the controls visible, and audit-ready evidence is one question away.
What Keypup Covers, and What It Doesn't
Keypup connects to your Git hosts (GitHub, GitLab, Bitbucket, Azure DevOps) and work trackers (Jira Cloud and Jira Data Center, Azure DevOps Boards, ClickUp, Trello, GitHub Projects), and keeps them in sync:
Continuous Data Collection
- Issues, pull requests, reviews, comments, commits on pull requests and activity events (status changes, assignments, merges)
- Each PR's approval count, required approvals and build status as reported by the Git host
- Links between PRs and issues, detected from issue keys or references in the PR title, branch name, PR body or commit messages
Keypup does not import deployment logs, access or permission changes, login and access logs, security scanner output (Dependabot alerts, Snyk), incident data (PagerDuty) or test results, and it never reads your source code. Those controls still need evidence from your identity provider, cloud platform, CI/CD and security tools. What Keypup can prove is everything that happens between an issue and a merged pull request, and that is where most change management and code review evidence lives.
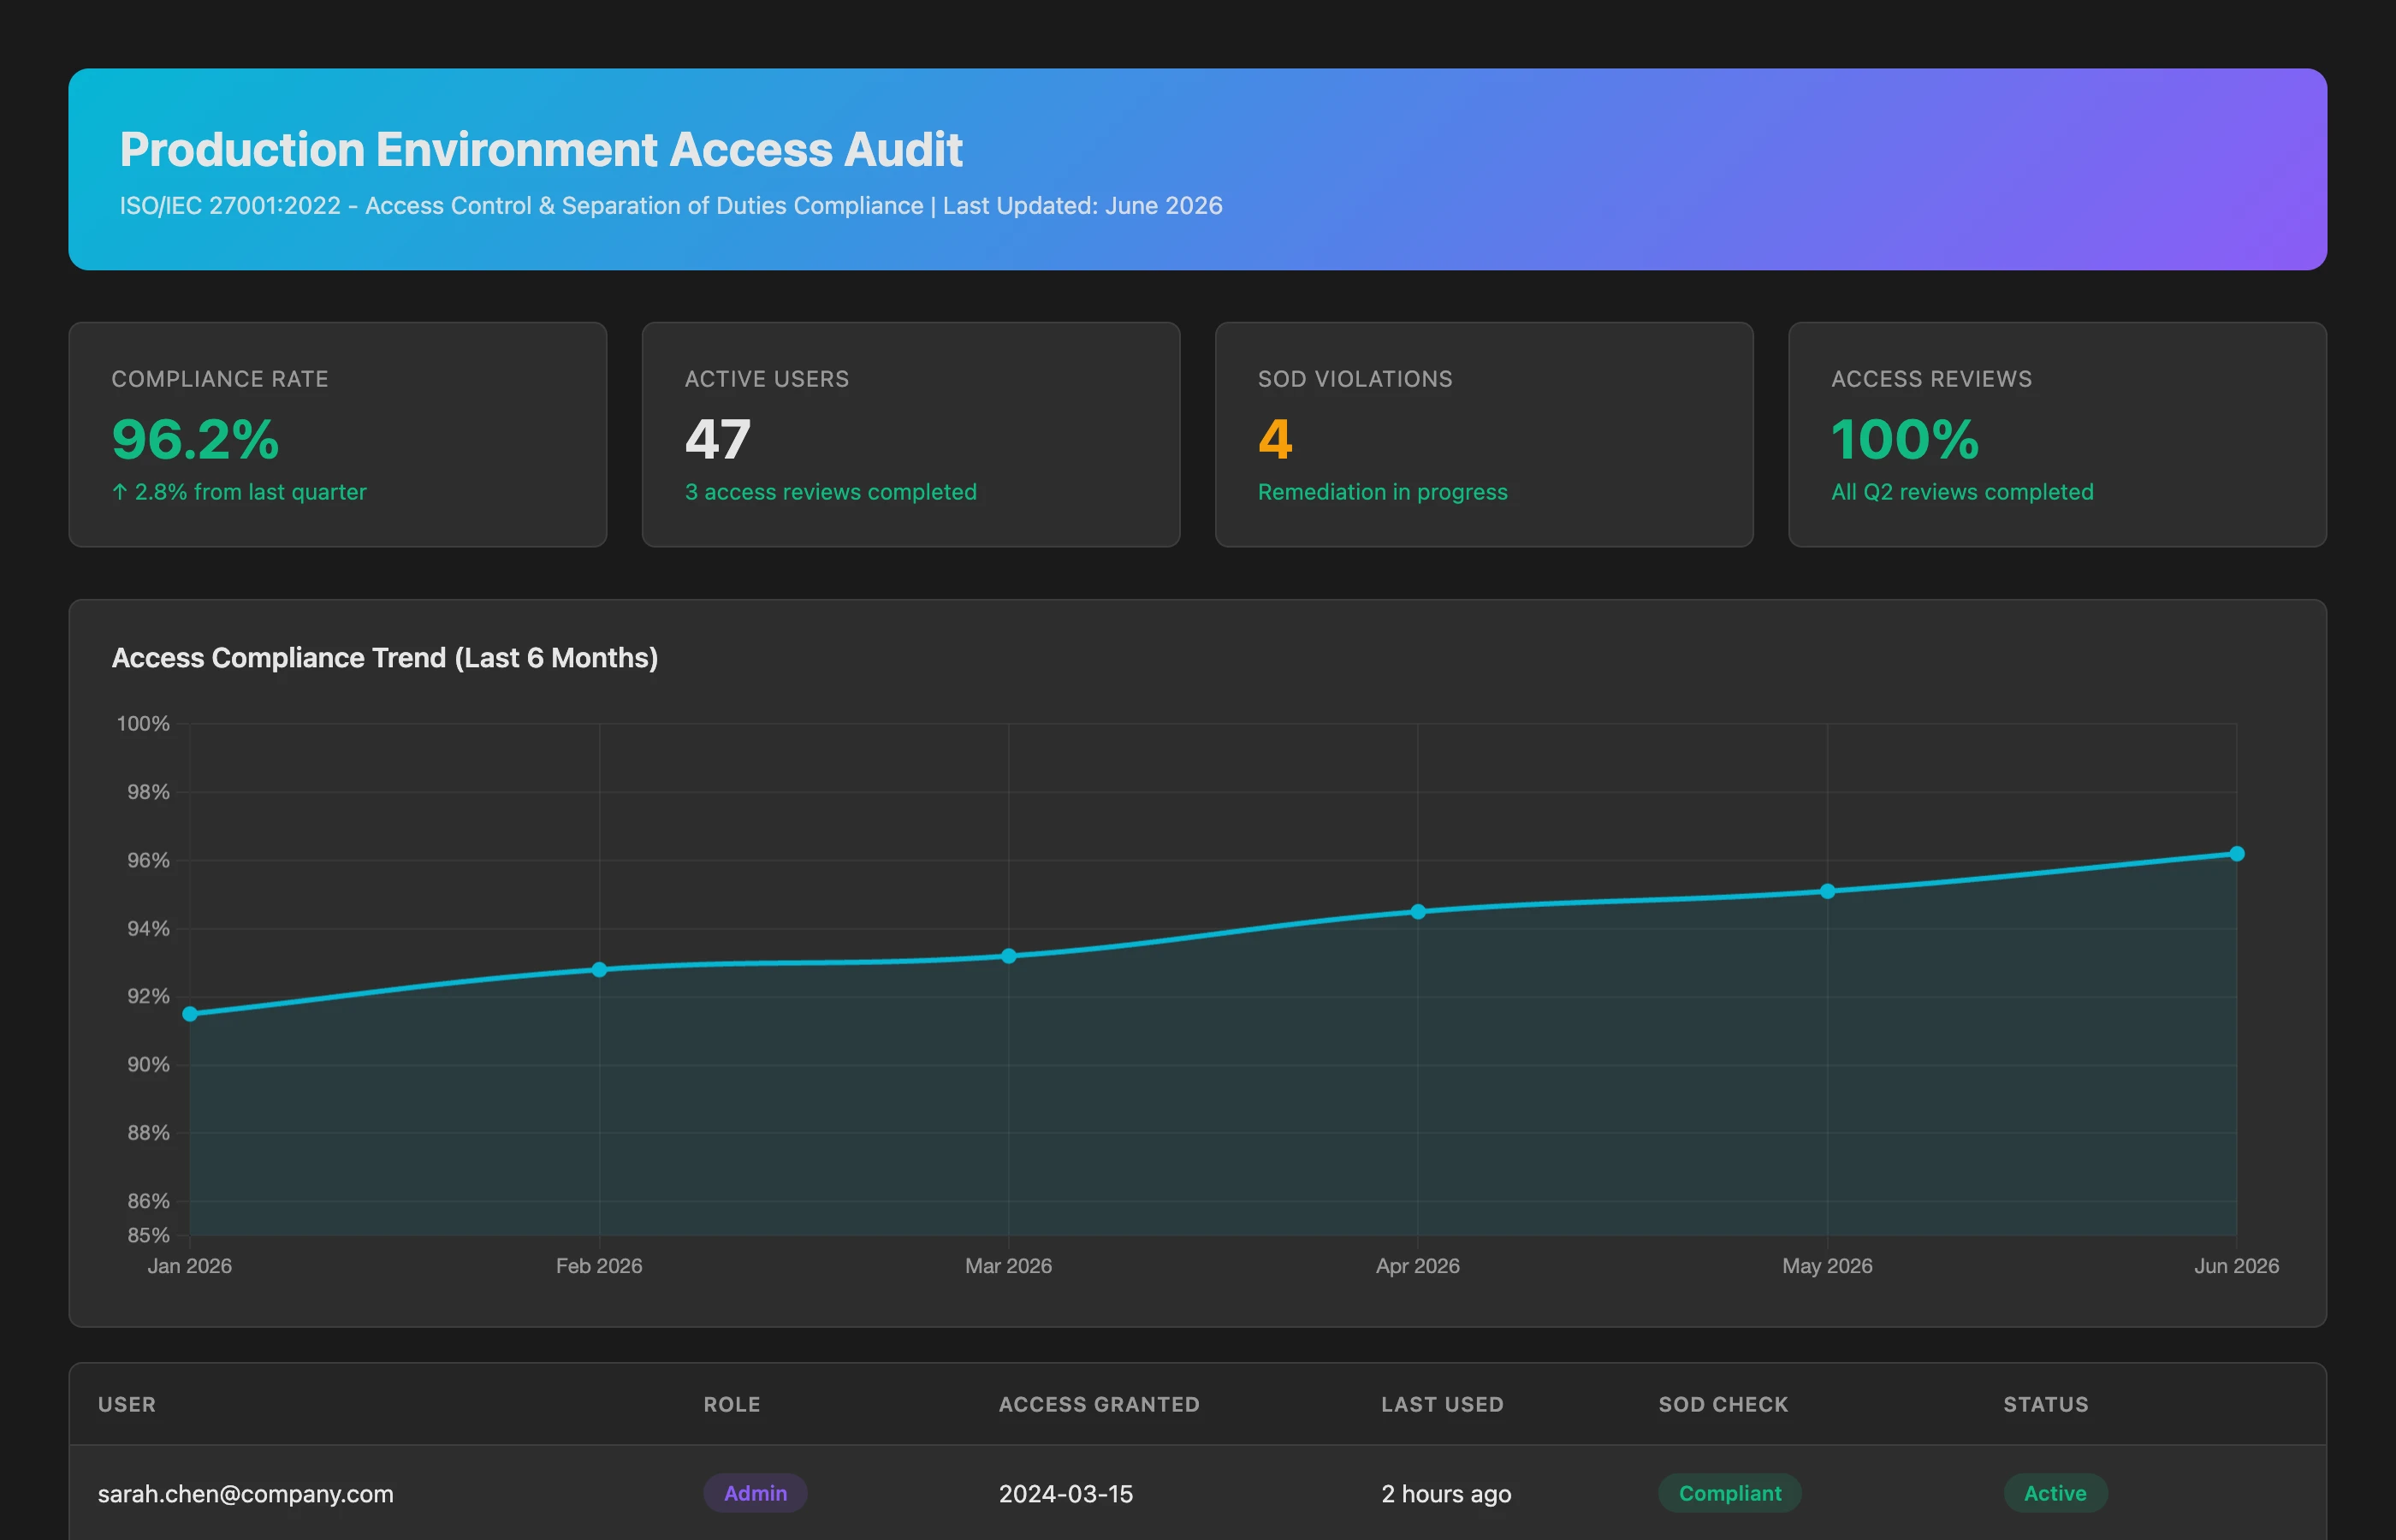
Compliance Dashboards (Keypup platform)
- The Audit & Compliance dashboard template: green build ratio, PR review ratio, PR compliance feed and project compliance score
- Custom compliance dashboards and insights built by the AI Agent from a plain-language request
- Trend analysis showing control effectiveness over time, with drill-down to the individual PRs that failed a control
On-Demand Evidence (Keypup MCP Server)
- Natural language queries from Claude, ChatGPT, Cursor, VS Code or Kiro to answer specific auditor questions for any time period
- Seven read-only tools: the MCP Server returns data, it cannot change anything in Keypup or in your tools
- Your team's AI Instructions (for example "a compliant PR has at least one approval from someone other than its author") are read by the AI client so every query applies the same definitions
Keypup has no alerting or scheduled reports, so "continuous monitoring" means a dashboard someone reviews on a fixed cadence, or a query your AI client runs when you ask it to. The MCP Server is included in Full Platform Access; the separate MCP & API plan gives query access without dashboards. See the MCP Server page and the setup guide.
Demonstrating ISO27001 Controls with Keypup
Let's walk through specific ISO27001 controls and show how Keypup supplies the SDLC part of the evidence:
A.8.31: Separation of Environments - Separation of Duties on Merges
Control requirement: Prove that developers cannot push changes to production on their own and that duties are appropriately segregated.
For the last 12 months, analyze pull requests merged into our production branches (main and release/*). Show: the number of PRs merged by their own author (self-merged), PRs merged without any approving review, and PRs merged with fewer approvals than the required approvals count. Break the results down by repository and by month, list the non-compliant PRs with author, merger and merge date, and show the percentage of merged PRs that were approved by someone other than their author.
This analysis gives auditors the merge side of separation of duties: proof that changes reaching your production branches were reviewed and approved by someone other than their author. Who holds production deployment permissions is a question for your cloud and CI/CD access controls, which Keypup doesn't see.
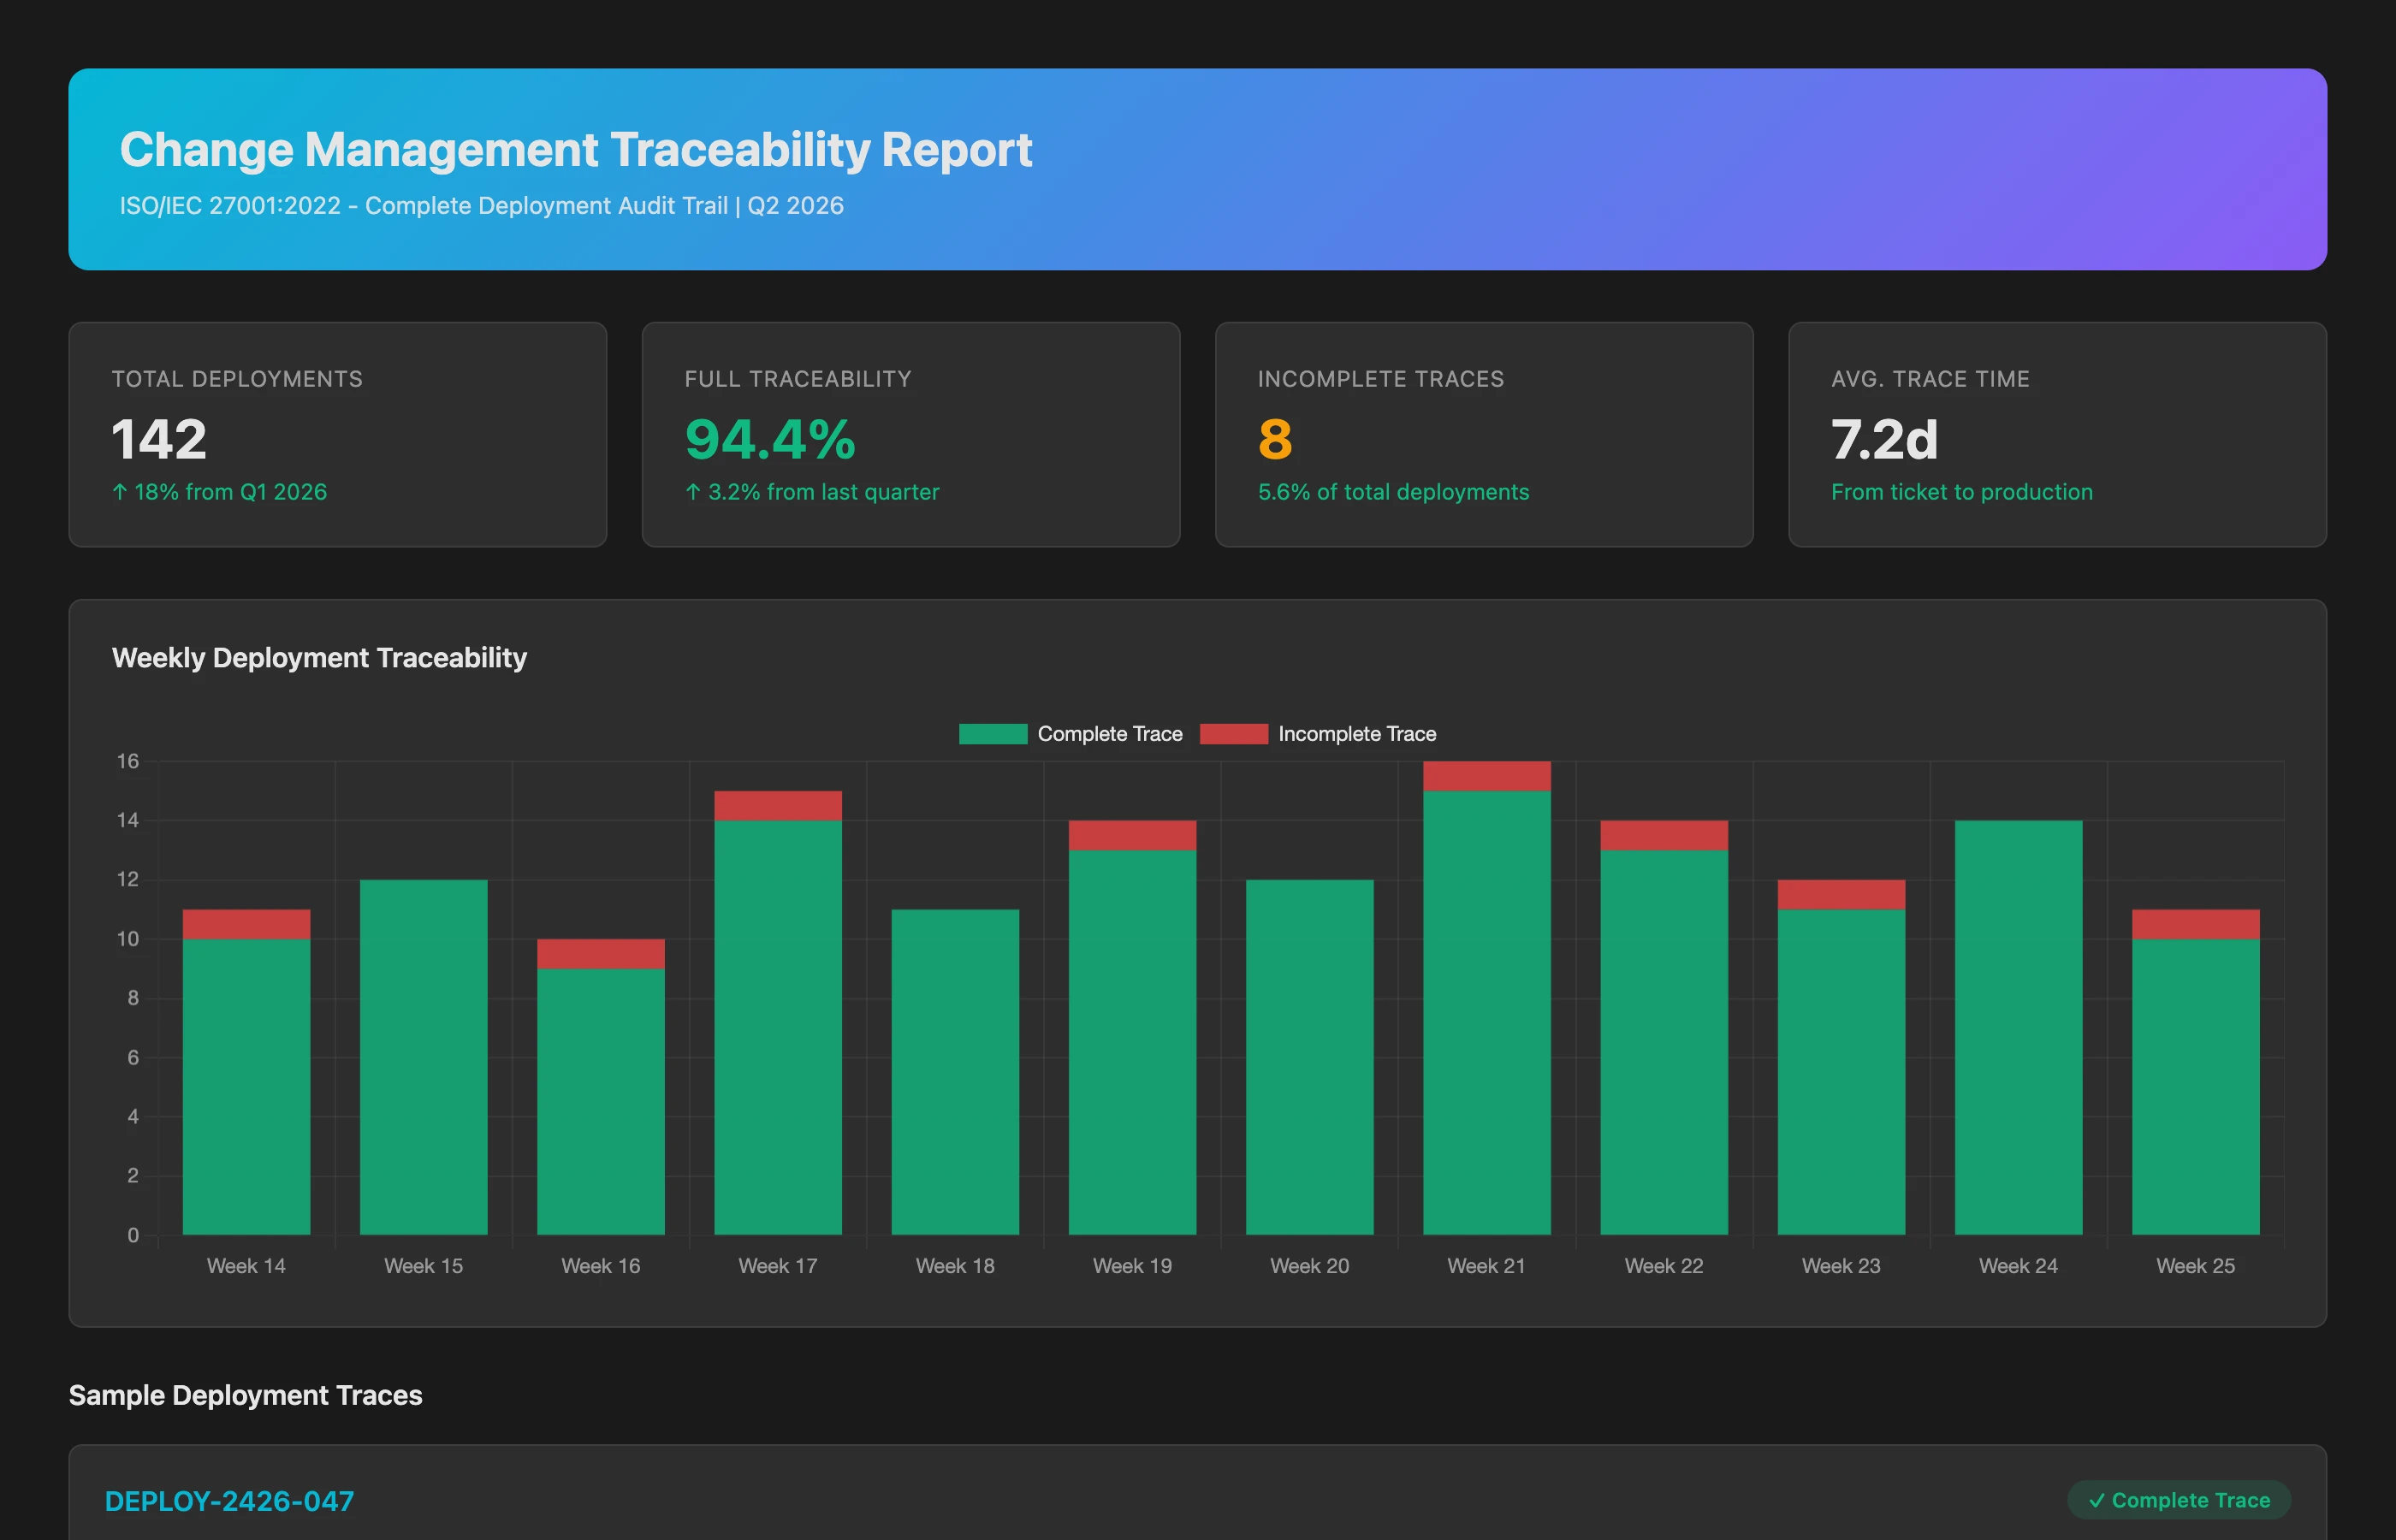
A.8.32: Change Management - Change Traceability
Control requirement: Demonstrate that all production changes are authorized, documented, tested, and traceable.
For Q2 2026, analyze all pull requests merged into main and show change management traceability. For each PR, show: the linked Jira issue (key, type and status), the reviewers and the number of approvals vs. required approvals, the build status at merge, and the merger. Flag any PR with no linked issue, no approving review, or a failed build status. Calculate the percentage of fully traceable PRs.
This single query produces an audit-ready view of traceability from ticket to merged change that would take days to compile manually. Note that Bitbucket Cloud no longer exposes the number of required approvals to Keypup, so on Bitbucket compare approvals against the minimum your policy sets.
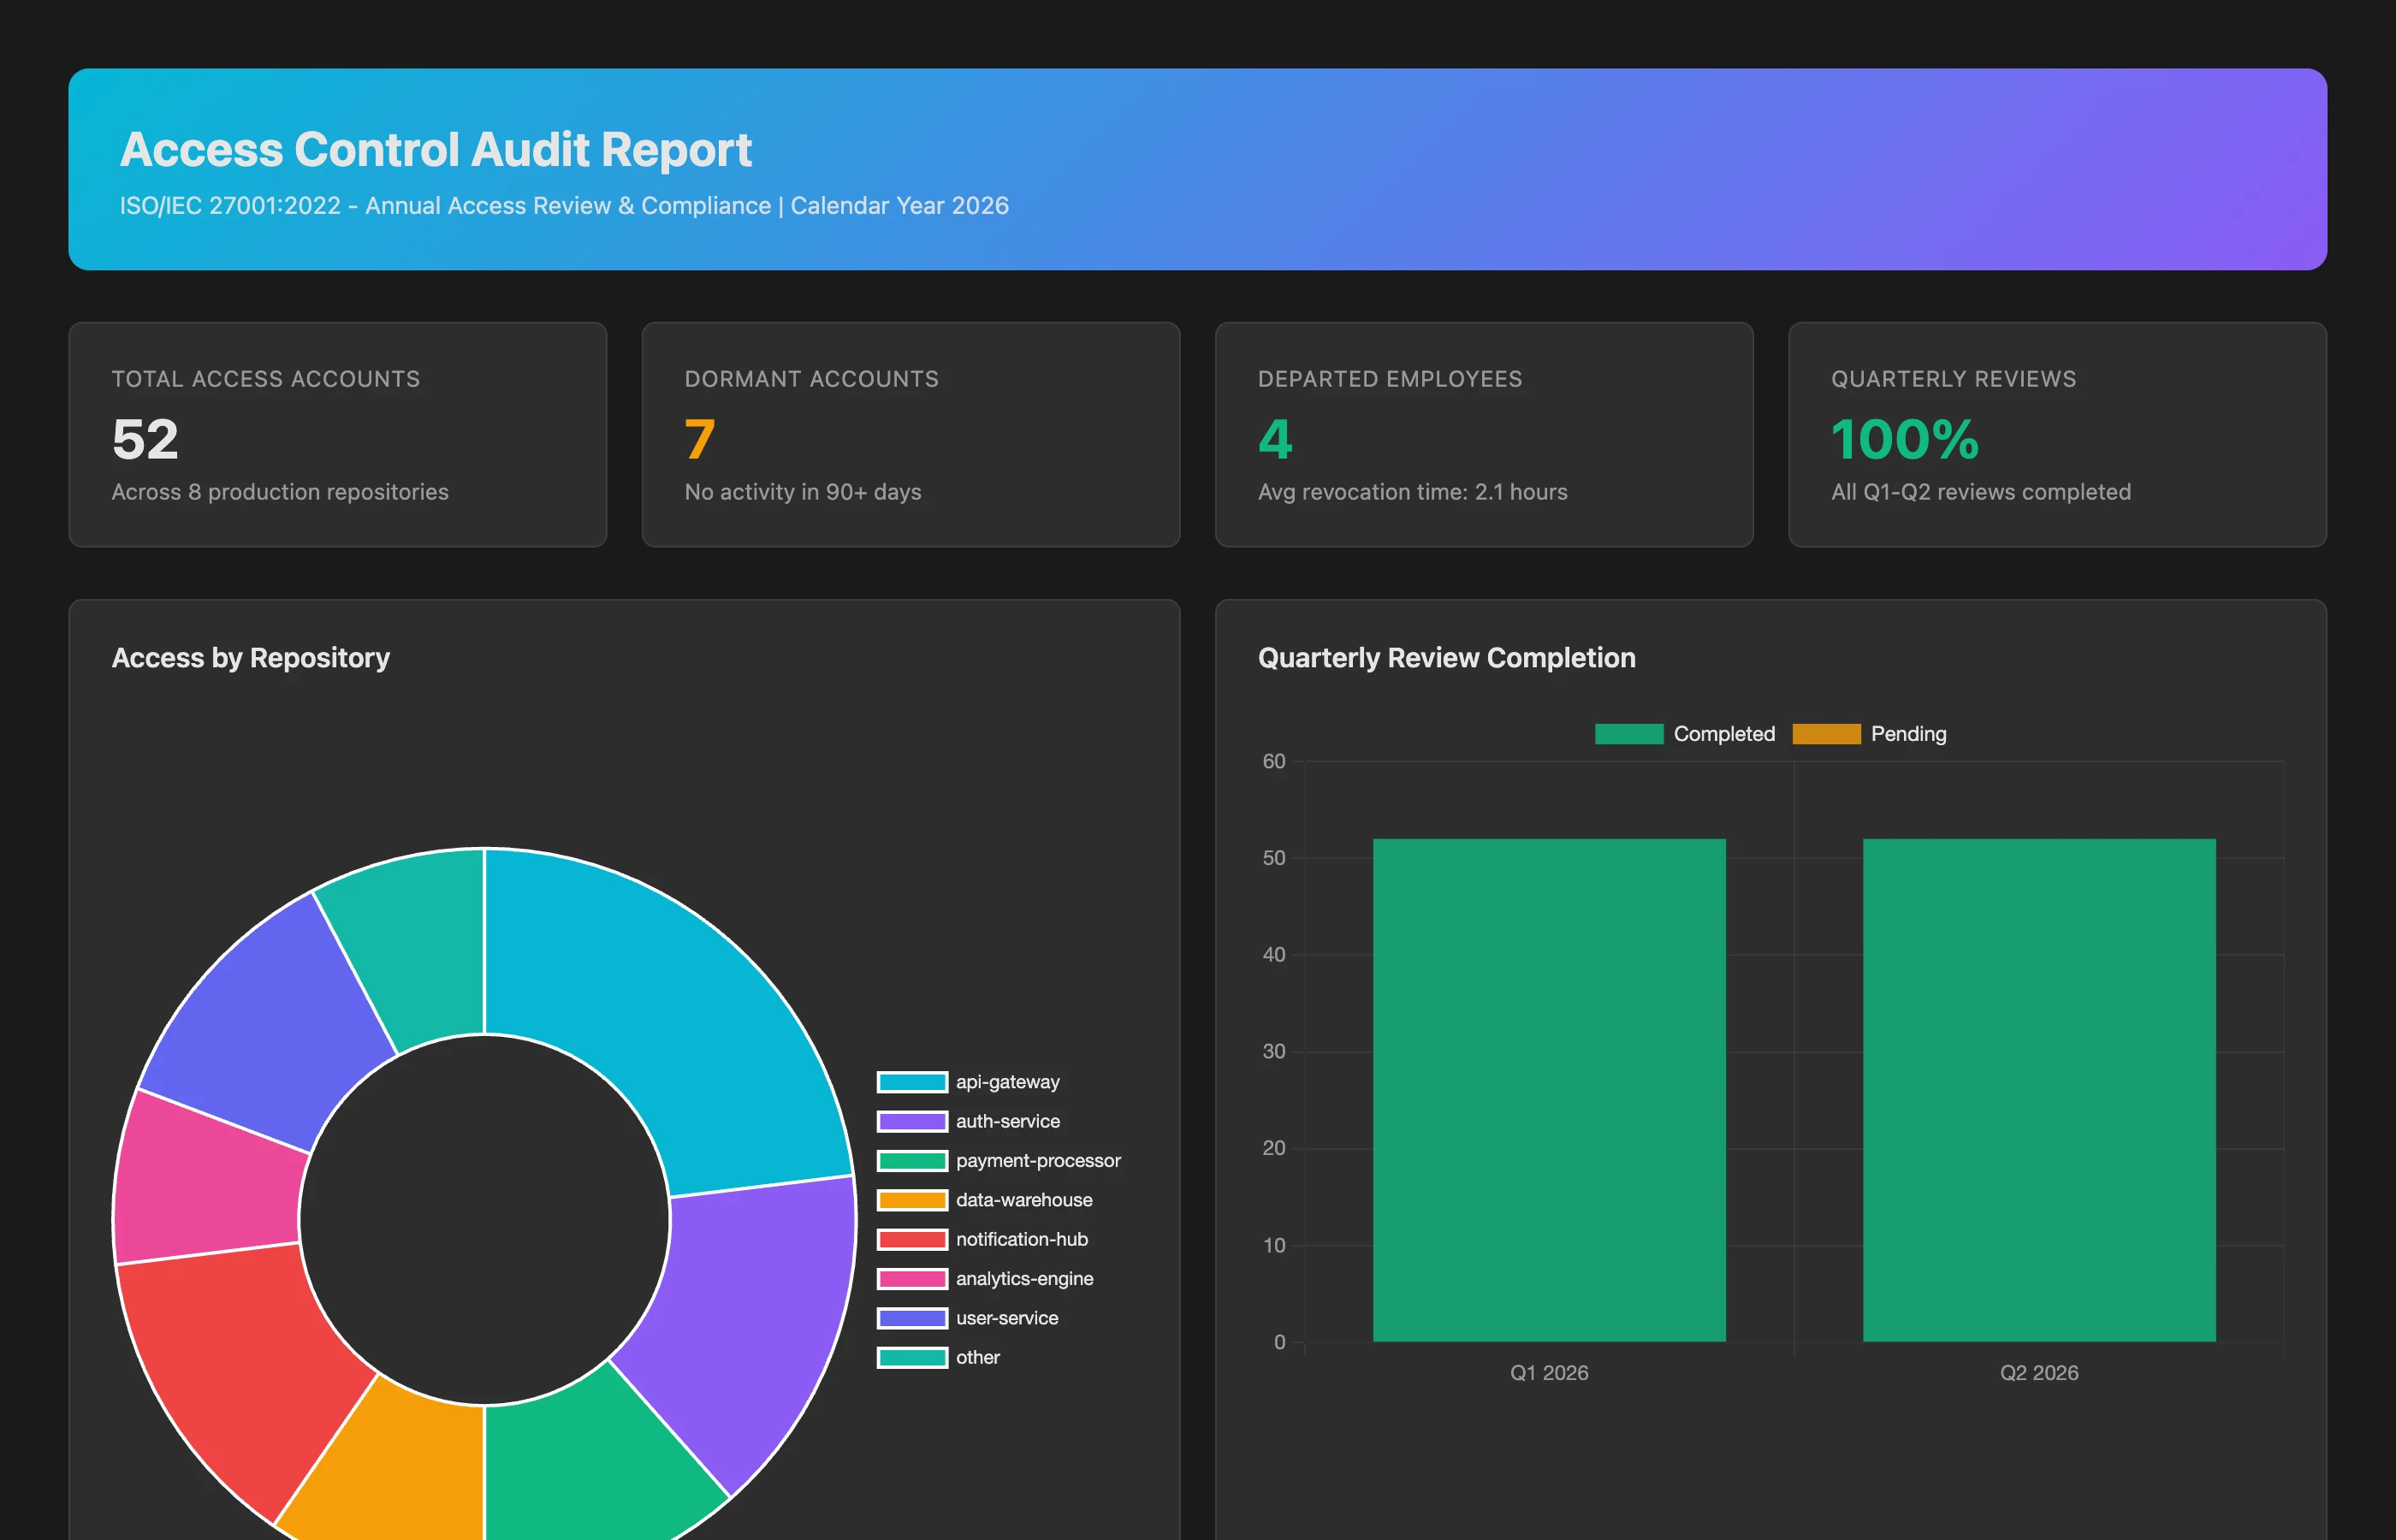
A.5.15 & A.5.16: Access Control and Identity Management
Control requirement: Show that access is granted on a need-to-know basis, regularly reviewed, and revoked when no longer needed.
To support our quarterly access review, list for each repository everyone who authored, reviewed or merged a pull request in 2026, with their last activity date. Flag contributors with no activity in the last 90 days, and anyone who merged PRs in a repository outside the teams defined in our AI Instructions.
Keypup doesn't hold your access rosters, grants or deprovisioning records: those come from your Git host's organization settings and your identity provider. What it adds to a quarterly access review is activity evidence, so reviewers can compare who has access with who actually works in each repository and spot dormant accounts worth revoking.
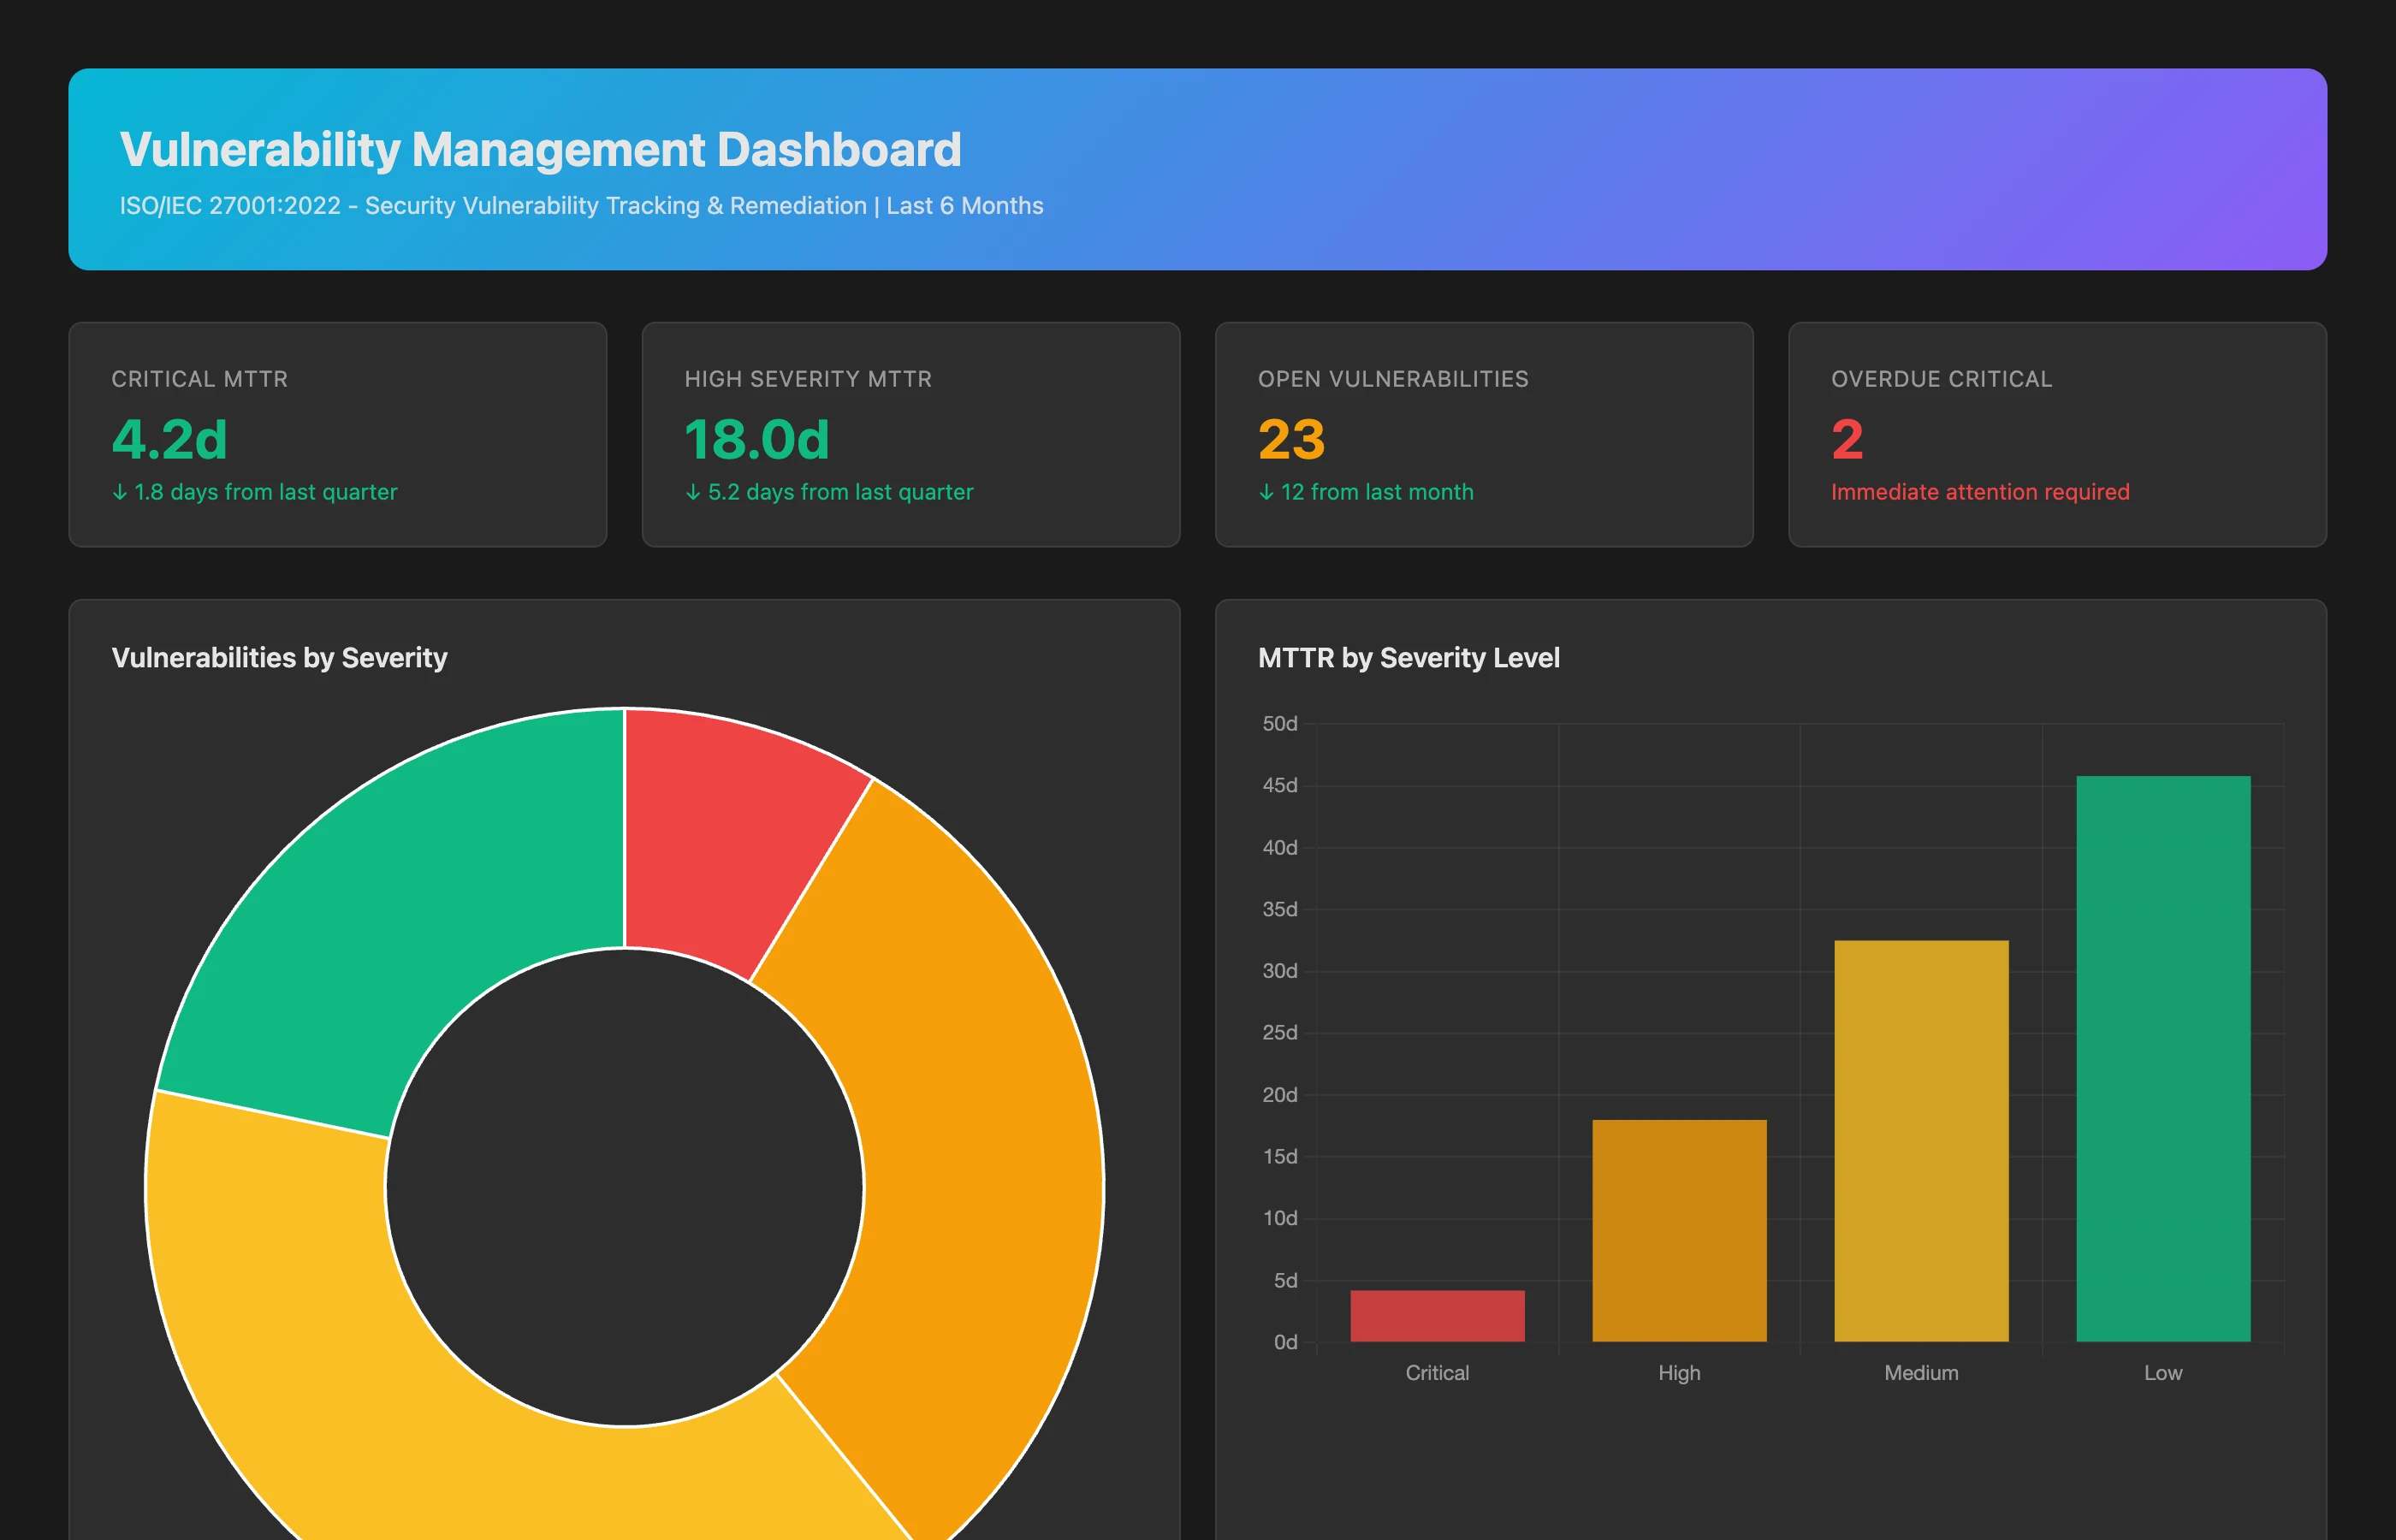
Control requirement: Prove that technical vulnerabilities are identified, tracked, and remediated in a timely manner.
Analyze vulnerability remediation for the last 12 months using issues labelled security or vulnerability in Jira. For each issue, show: key, priority, creation date, status, resolution date and time to remediation, plus the linked pull requests that fixed it. Calculate mean time to remediate by priority. Flag any critical-priority issue open longer than 7 days or high-priority issue open longer than 30 days. Separately, show the time to merge for pull requests opened by Dependabot. Show the trend over time: is remediation time improving or degrading?
Keypup doesn't import scanner findings, so this works when your process records vulnerabilities as labelled issues in your work tracker (many teams route scanner findings into Jira), and when dependency updates arrive as pull requests. It then provides comprehensive evidence that remediation happens within your policy's deadlines.
Demonstrating SOC2 Trust Services Criteria with Keypup
SOC2 Type II requires proving that controls operated effectively throughout the audit period (typically 12 months). Let's see how Keypup provides the SDLC part of this evidence:
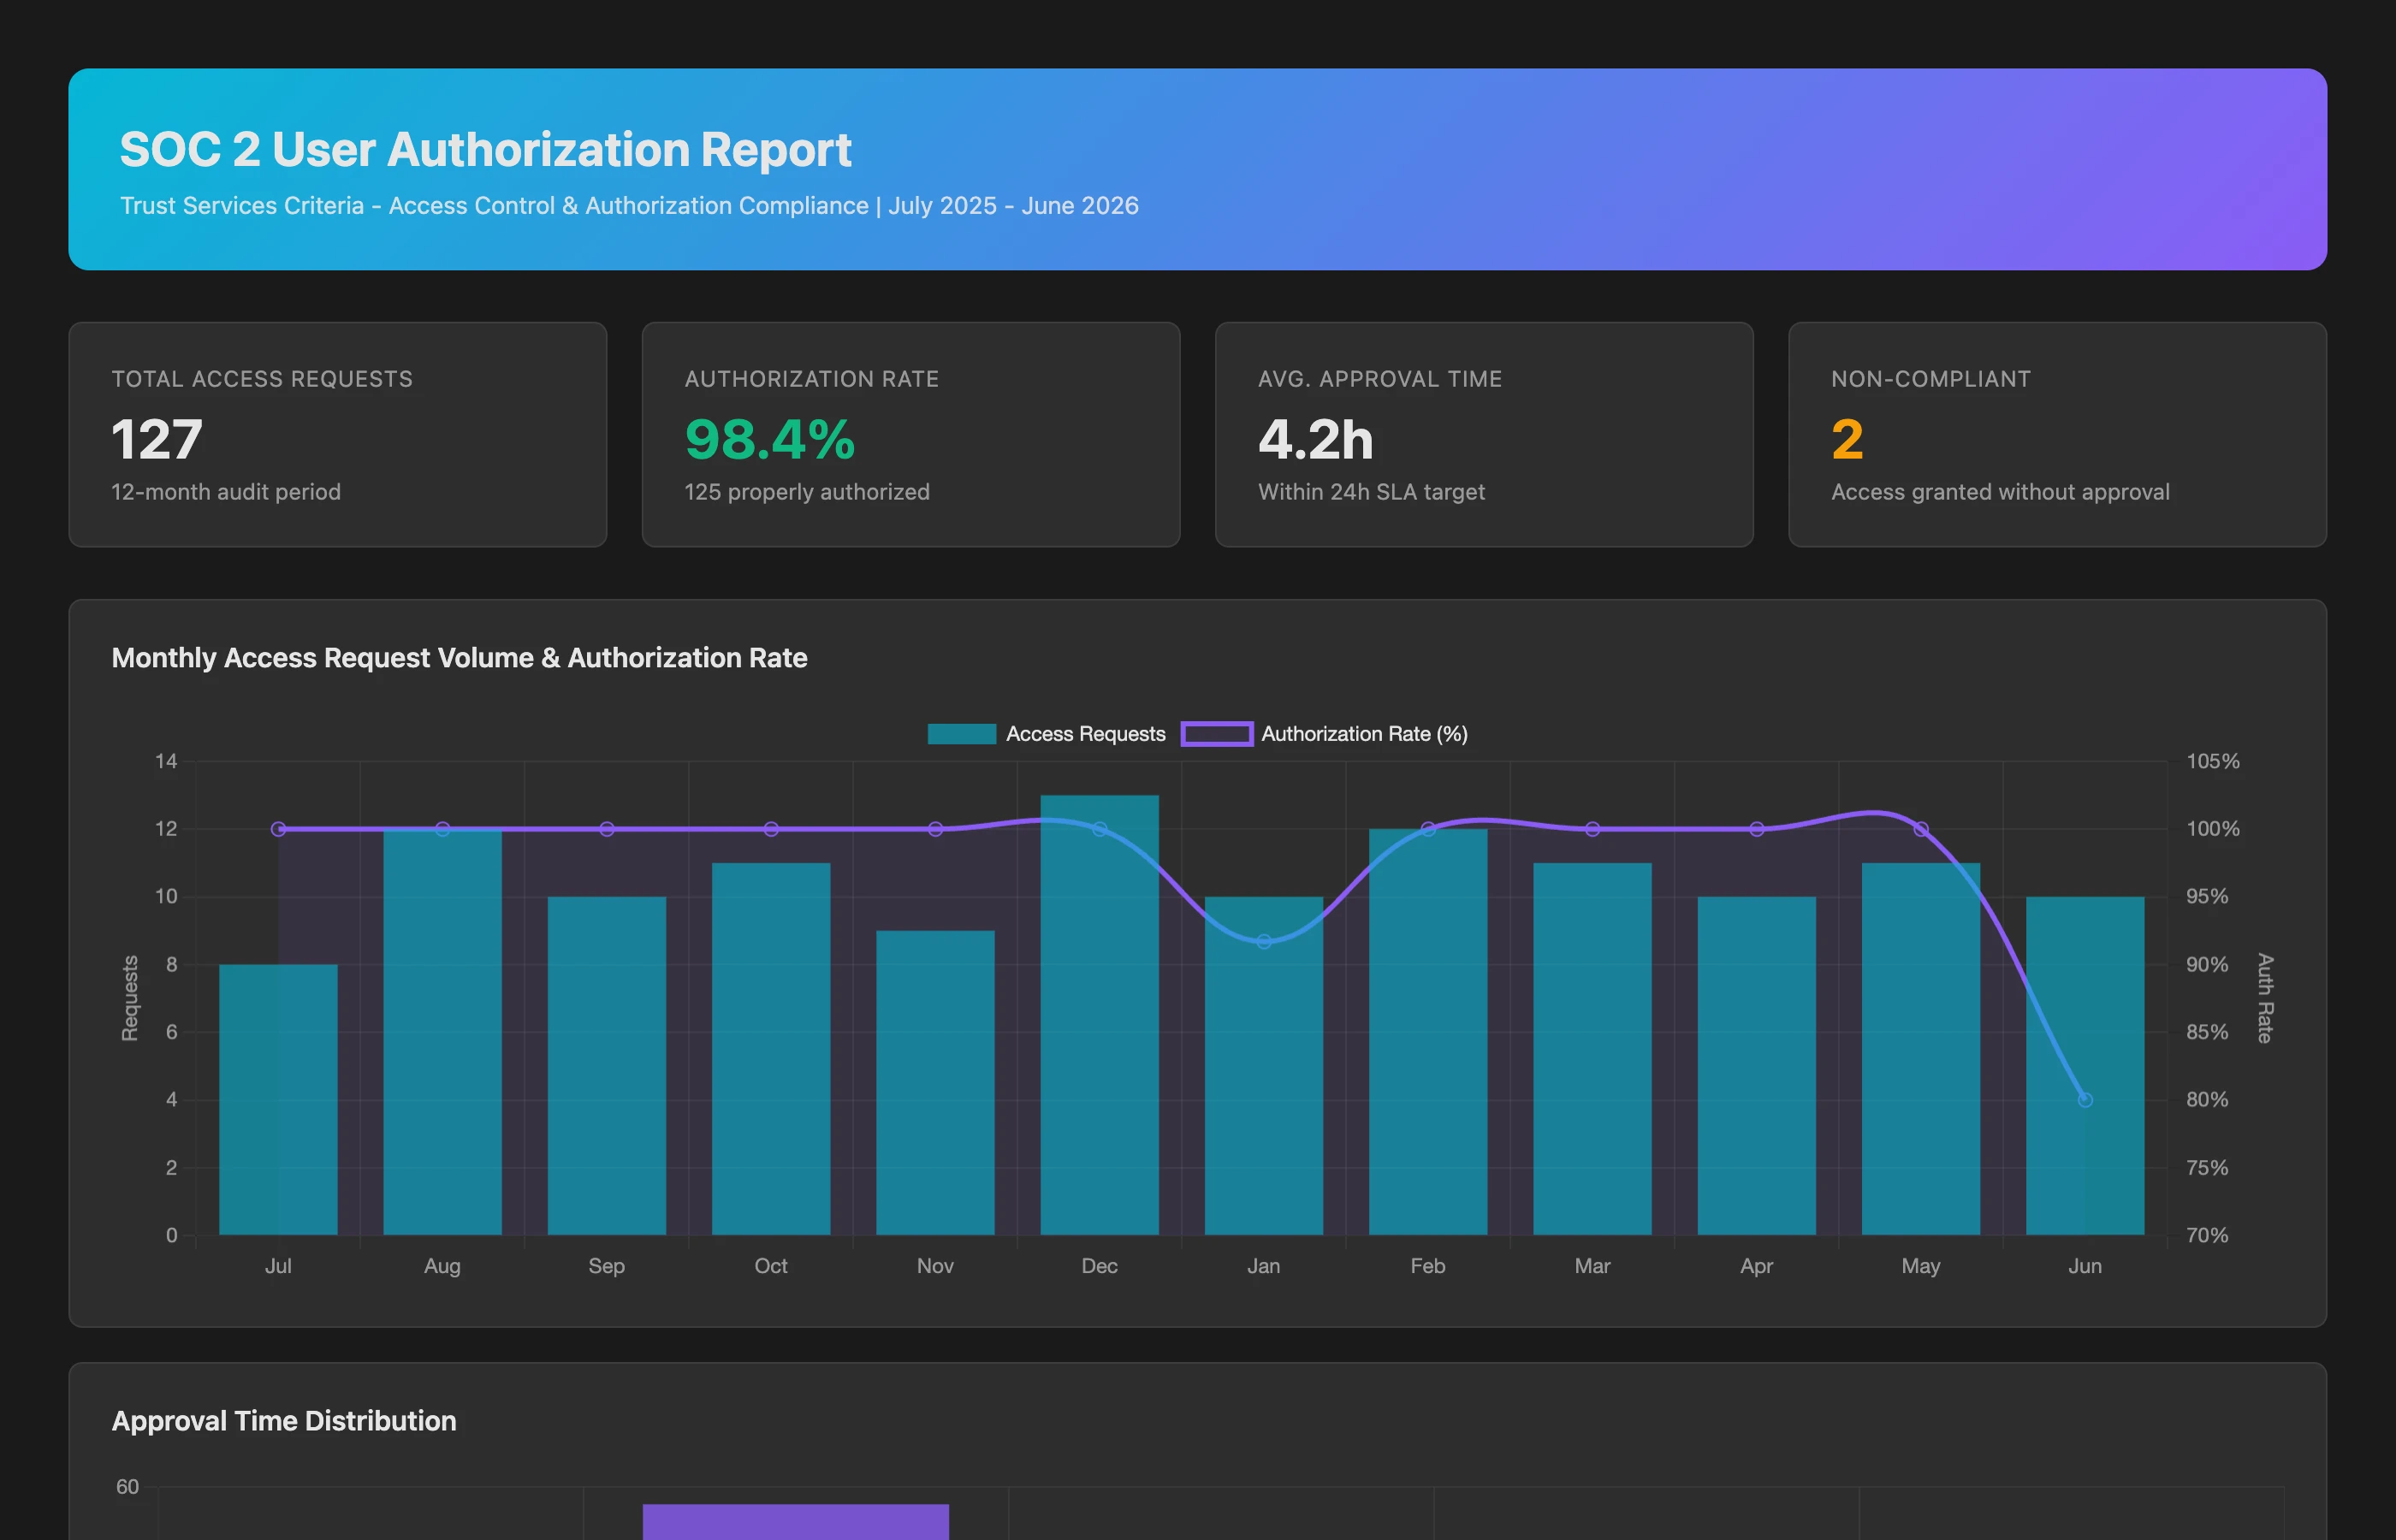
CC6.6: Logical Access - Authorized Approval of Changes
Control requirement: Prove that changes are authorized by the right people and that authorization follows documented procedures.
For the SOC2 audit period (July 2025 - June 2026), generate a change authorization report for pull requests merged into main. For each month and repository, show: the number of merged PRs, approvals received vs. required approvals, the people who approved them, and PRs approved only by people outside the authorized reviewers listed in our AI Instructions. Flag PRs merged with no approving review, or with fewer approvals than required. Show the percentage of merged PRs that followed the approval policy.
This demonstrates systematic authorization of code changes operating over the full audit period. User provisioning and credential issuance are evidenced from your identity provider, not from Keypup.
CC6.8: Access Control - Unauthorized Change Prevention
Control requirement: Show that changes to production systems are controlled, monitored for anomalies, and that unauthorized changes are detected and remediated.
For the SOC2 audit period, find unusual merge activity on our production branches: PRs merged outside working hours or at weekends, PRs merged by someone who isn't among the repository's usual mergers, PRs merged within 10 minutes of being opened, and PRs merged without an approving review. For each, show the PR, author, merger, approvals, linked issue and merge time, and summarize the counts by month.
Auditors want proof that change monitoring actually works. This provides operational evidence across the full period for the code path to production. Login attempts, access logs and access from unexpected locations are recorded by your Git host's audit log and your identity provider, which Keypup doesn't import.
CC7.2: System Monitoring - Anomaly Detection and Response
Control requirement: Demonstrate that system components are monitored for anomalies and that anomalies trigger appropriate response procedures.
Generate an SDLC anomaly report for the SOC2 audit period. Identify: code review bypasses (PRs merged without an approving review, self-merged PRs), rubber-stamp patterns (approvals submitted within 5 minutes of the review request on PRs over 500 lines changed, with no review comments), PRs merged with a failed build status, and spikes in issues labelled security or incident. For issues labelled security or incident, show creation date, priority, assignee, resolution date and time to resolve. Calculate mean time to resolve by priority and month.
Reviewed on a regular cadence, these figures show your SDLC controls operate continuously, not just when auditors are watching. Incident response itself is evidenced only as far as you track incidents as labelled issues in your work tracker; Keypup has no incident or monitoring-tool data.
CC8.1: Change Management - Complete Documentation
Control requirement: Show that changes are authorized, documented, tested, and approved before deployment.
Provide change management evidence for the SOC2 audit period. For a random sample of 40 pull requests merged into main, show for each: the linked Jira issue (key, type, summary), the PR (title, lines added and deleted, link), the reviewers, number of review comments, approvals vs. required approvals with approval timestamps, the build status at merge, the merger and the merge date. Calculate the percentage of PRs with complete documentation (linked issue, approval, successful build). Flag any incomplete change records.
Rather than spending weeks assembling this evidence manually, the Keypup MCP Server returns it in minutes for any requested sample. Design review records, detailed test results, deployment logs and post-deployment validation still come from the tools that hold them.
The ROI of Automated SDLC Compliance: Time and Cost Savings
Let's estimate the financial impact of automating SDLC evidence for ISO27001 and SOC2 Type II compliance. The figures below are a hypothetical illustration built from typical industry cost ranges, not measured Keypup customer results: replace them with your own consultant quotes, audit fees and loaded salary rates.
Initial Certification Time and Cost Reduction (Illustrative Estimate)
Traditional approach (manual evidence collection):
- Timeline: 8-13 months from kickoff to certification
- Consultant fees: $15K-$40K for gap analysis + implementation support
- Internal time: 600-1000 hours of engineering/security team time
- Audit fees: $20K-$60K depending on company size and complexity
- Total cost: $150K-$400K
Automated SDLC evidence approach (hypothetical, with Keypup covering code review and change management evidence):
- Timeline: 4-7 months (assumes faster evidence availability for SDLC controls)
- Consultant fees: $10K-$25K (assumes less time needed since SDLC evidence is already organized)
- Internal time: 200-400 hours (assumes a large cut in SDLC evidence collection overhead)
- Audit fees: $15K-$45K (assumes auditors spend less time on SDLC samples)
- Keypup subscription: priced per activated project (Full Platform Access) or per 100,000-record bucket (MCP & API plan); see Keypup pricing for your team's figure
- Total cost: $60K-$150K plus the Keypup subscription
Illustrative first-year savings: the difference between the two ranges, minus your Keypup subscription. Your actual result depends on how much of your evidence burden is SDLC evidence.
Calculate a hypothetical ROI of automating SDLC evidence for initial ISO27001 and SOC2 Type II certification, using only the figures I supply: consultant fees, internal hours at a $125/hour loaded rate, audit fees, and our Keypup subscription cost. Compare the manual approach with the automated approach (reduced consultant time, reduced internal time, lower audit fees, plus Keypup subscription). Show the time savings (months faster), cost savings (dollars saved), and ROI percentage, and a break-even analysis. To ground the internal-hours estimate, count the merged pull requests in our audit scope over the last 12 months.
Ongoing Maintenance Cost Reduction (Illustrative Estimate)
Traditional approach (annual recertification):
- Continuous evidence collection: 200-300 hours annually of engineering time
- Quarterly access reviews: 40-60 hours annually
- Audit preparation: 100-150 hours assembling evidence for annual audit
- Consultant support: $20K-$40K for ongoing compliance management
- Annual audit fees: $15K-$40K
- Total annual cost: $80K-$150K
Automated SDLC evidence approach (hypothetical, always-ready compliance):
- Continuous evidence collection: SDLC evidence syncs automatically; a weekly dashboard review of a few hours a month remains
- Quarterly access reviews: 10-20 hours annually (assumes activity data speeds up reviews; access rosters still come from your identity provider)
- Audit preparation: 20-40 hours (assumes SDLC evidence is available on demand)
- Consultant support: $5K-$15K (assumes minimal support needed)
- Annual audit fees: $12K-$30K (assumes auditors work faster)
- Keypup subscription: per activated project or per 100,000-record bucket, see pricing
- Total annual cost: $30K-$70K plus the Keypup subscription
Illustrative annual maintenance savings: the gap between the two ranges, minus your subscription. Multiply by three for a typical certification cycle, and check the assumptions against your own costs.
Calculate a hypothetical 3-year total cost of ownership (TCO) for maintaining ISO27001 and SOC2 Type II compliance, using the cost figures I supply. Compare: the manual approach (annual recertification costs, evidence collection overhead, consultant fees) vs. the automated SDLC evidence approach (reduced overhead, lower audit fees, plus our Keypup subscription). Show year-by-year costs, cumulative savings, and 3-year ROI. Include a sensitivity analysis at different team sizes (20 devs, 50 devs, 100 devs), using our current number of active pull request authors as the starting point.
Beyond Cost: Strategic Benefits
Financial savings are significant, but automated compliance provides additional strategic value:
Always audit-ready: No more scrambling before audits—SDLC evidence is continuously available
Up-to-date compliance visibility: Know the posture of your SDLC controls at any time, not just during audits
Faster sales cycles: Quickly provide SDLC compliance evidence to prospects during due diligence
Reduced compliance risk: A regular dashboard review surfaces control failures within days, not months later
Engineering productivity: Developers focus on products, not compliance spreadsheets
Scalability: Compliance overhead doesn't increase linearly as team grows
Best Practices: Implementing Continuous SDLC Compliance
Here is a suggested implementation plan for continuous SDLC compliance:
Phase 1: Baseline Assessment (Week 1-2)
Objective: Understand current state and compliance gaps.
Activities:
- Connect your Git hosts and work trackers to Keypup, then connect your AI client to the Keypup MCP Server (one-click OAuth from the MCP Setup page in the Keypup sidebar)
- Run a baseline analysis of the SDLC controls Keypup can evidence
- Identify control gaps and non-compliant activities
- Prioritize remediation based on audit risk
Keypup MCP queries to run:
- Contributor activity per repository, to support your access review
- Last 12 months of change traceability (merged PRs with linked issues, approvals and build status)
- Remediation time for issues labelled security or vulnerability
- Code review compliance rates (self-merged PRs, PRs merged without approval)
- Approvals vs. required approvals per repository
Phase 2: Control Implementation (Week 3-8)
Objective: Implement missing controls and remediate gaps.
Activities:
- Implement technical controls (MFA, role-based access, branch protection with required approvals, etc.)
- Document policies and procedures
- Write your compliance definitions into your team's AI Instructions in Keypup
- Build your compliance dashboard in the Keypup platform
- Train team on new processes
Keypup configuration:
- Describe your compliance rules in AI Instructions (e.g., "critical-priority security issues must be resolved within 7 days"), so the AI Agent and every MCP query apply the same definitions
- Start from the Audit & Compliance dashboard template, or ask the AI Agent to build a dashboard for your controls
- Agree who reviews the dashboard and how often, since Keypup doesn't send alerts
Phase 3: Evidence Collection (Week 9-12)
Objective: Build complete audit trail for certification period.
Activities:
- Add the insights auditors expect to your compliance dashboard in Keypup
- Prepare the questions you'll ask through the MCP Server for each auditor sample request
- Run sample audits to validate evidence completeness
- Create narrative documentation to accompany quantitative evidence
Key evidence to prepare:
- Contributor activity per repository for quarterly access reviews
- Change management traceability for sampled pull requests
- Remediation records for security-labelled issues
- Code review and approval compliance
- Control effectiveness trends
Phase 4: Pre-Audit Validation (Week 13-14)
Objective: Ensure audit readiness before engaging auditors.
Activities:
- Run mock audit using Keypup evidence
- Identify any evidence gaps or control weaknesses
- Remediate issues before formal audit
- Prepare auditor briefing materials
Objective: Successfully complete certification audit.
Activities:
- Walk auditors through your Keypup compliance dashboard
- Respond to auditor sample requests quickly using natural language queries through the MCP Server
- Provide drill-down detail for any flagged issues
- Complete audit with minimal back-and-forth
Phase 6: Continuous Maintenance (Ongoing)
Objective: Maintain always-ready compliance state.
Activities:
- Review the compliance dashboard weekly for violations
- Investigate and remediate policy violations promptly
- Run quarterly access reviews with contributor activity data from Keypup and access rosters from your identity provider
- Update your AI Instructions as controls evolve
- Conduct annual recertification audits in days, not weeks
Common Pitfalls and How to Avoid Them
Organizations implementing SDLC compliance often encounter these challenges:
Pitfall 1: Treating Compliance as a One-Time Project
We spent 9 months getting ISO27001 certified, then immediately stopped paying attention to compliance. A year later, when surveillance audit came around, we discovered our code review compliance had dropped from 98% to 72%. We had to scramble to explain why and implement remediation plans. Continuous monitoring would have caught this degradation immediately.
Solution: Use a Keypup compliance dashboard for a weekly compliance review, with trend insights that make control degradation visible.
Pitfall 2: Over-Focusing on Documentation, Under-Focusing on Operations
Many teams write beautiful policies but don't implement operational controls to match.
Solution: Use Keypup to validate that documented procedures actually match operational reality. If your policy says "all PRs require 2 approvals," a Keypup query comparing approvals with required approvals proves whether that's true or aspirational.
Pitfall 3: Siloing Compliance Away from Engineering
When compliance becomes "someone else's job," engineers don't understand or follow controls.
Solution: Integrate compliance visibility directly into engineering workflows. Use Keypup dashboards in team meetings to show control effectiveness as an engineering KPI.
Pitfall 4: Manual Evidence Collection Instead of Automation
Some teams use Keypup for monitoring but still manually export data for audits.
Solution: Answer auditor requests directly from your Keypup dashboards and MCP queries, and agree with your auditor early on which SDLC evidence they will accept in that form.
Pitfall 5: Ignoring Trend Analysis
Point-in-time compliance snapshots miss degrading controls.
Solution: Track compliance metrics over time with trend insights in your Keypup dashboard. Identify controls that are weakening before they fail audits.
Conclusion: From Compliance Burden to Competitive Advantage
ISO27001 and SOC2 Type II certifications are increasingly non-negotiable for software companies selling to enterprise customers or raising institutional capital. But achieving and maintaining these certifications doesn't have to be a painful, expensive burden that diverts engineering resources from product development.
By treating SDLC compliance as an operational capability rather than a periodic audit event, and by keeping SDLC evidence continuously available in Keypup dashboards and through the Keypup MCP Server, organizations can:
- Shorten the evidence phase of initial certification for code review and change management controls
- Reduce consultant and internal time spent assembling SDLC evidence (see the illustrative estimate above)
- Lower ongoing maintenance effort by replacing one-off scripts with reusable dashboards and queries
- Cut manual SDLC evidence collection for every auditor sample request
- Maintain an always-ready audit state with up-to-date compliance visibility
- Scale compliance without scaling overhead as engineering teams grow
Key takeaways:
ISO27001 and SOC2 impose significant SDLC-specific requirements including access control audits, change management traceability, vulnerability remediation tracking, and continuous monitoring—all of which require extensive evidence that lives in your development tools.
Traditional manual approaches are expensive and don't scale, requiring 600-1000 hours of effort and $150K-$400K for initial certification, with ongoing maintenance costs of $80K-$150K annually.
Automated continuous compliance monitoring transforms the economics, reducing evidence overhead while improving compliance posture and audit readiness.
Keypup provides SDLC-specific compliance evidence: dashboards in the Keypup platform for continuous visibility, and the read-only Keypup MCP Server for natural language queries that return audit-ready evidence on demand, replacing custom scripts, spreadsheets, and manual data compilation for code review and change management controls.
The ROI can be substantial: model it with your own consultant, audit and salary figures, and add strategic benefits like faster sales cycles and reduced compliance risk.
The question for software development organizations isn't "Should we automate SDLC compliance?" but rather "Can we afford not to?" As certification requirements become more stringent and audits more frequent, the gap between automated and manual approaches will only widen.
Continuous SDLC compliance doesn't just save money—it transforms security certification from a painful checkbox exercise into a strategic capability that accelerates sales, enables growth, and demonstrates operational excellence to customers and investors.
To get started, connect your AI client to the Keypup MCP Server with one-click OAuth 2.1 sign-in (tokens expire, and every tool is read-only), or follow the MCP setup guide. Keypup is priced per activated project on Full Platform Access, which includes dashboards and the MCP Server, or per 100,000-record bucket on the MCP & API plan: see pricing. And because Keypup holds ISO 27001 and SOC 2 Type II itself, it fits into your vendor review: details are on the Trust Center.